01
Cyber risk and gap assessment
Policies, asset inventory, access control, backups, logging and vendors reviewed against best practice, with every gap rated by likelihood and impact.
Independent Cyber Security Audits for Australian Businesses
Find out where you are exposed before an attacker, an insurer or a customer does. CyberSapiens Lead Auditors review your controls, test your systems and your people, score your Essential Eight maturity and hand you a risk-ranked action plan your board can act on.
PhishCare is a product of CyberSapiens. Cyber security audits are delivered by CyberSapiens. Last updated .
6 areas
audited by one team
ML0 to ML3
Essential Eight maturity scored
1 report
with a risk-ranked action plan
24 hours
to your fixed-price quote
A cyber security audit is an independent review of how well your business protects its systems, data and people. It checks your policies and controls against a recognised framework, tests your defences, and ends with a report that ranks every gap by risk and tells you what to fix first.
For most small and mid-sized Australian businesses, a focused audit takes 2 to 6 weeks from kick-off to final report, depending on scope and whether penetration testing is included. In Australia, audits usually measure you against the ASD's Essential Eight maturity model, alongside ISO 27001 or SOC 2 when your customers ask for them.
Google review of CyberSapiens · SOC 2 Type II audit
"We especially appreciated the valuable guidance and practical inputs provided during the security review. They were always available to clarify our questions and helped make the overall audit process simple and efficient."
If any of these apply, an independent audit is the fastest way to know where you stand and to prove it to others.
Obligations are growing: since 30 May 2025, businesses with turnover over AUD 3 million must report ransomware payments within 72 hours under the Cyber Security Act 2024, and eligible data breaches must be reported under the OAIC's Notifiable Data Breaches scheme.
One audit, six areas. We scope only what you need, so a small business is not paying for an enterprise review.
01
Policies, asset inventory, access control, backups, logging and vendors reviewed against best practice, with every gap rated by likelihood and impact.
02
Each of the eight ASD mitigation strategies scored from Maturity Level 0 to 3, with the steps to reach your target level.
03
VAPT on your network, cloud and web applications to prove which weaknesses can actually be exploited, followed by a retest.
04
A PhishCare phishing simulation shows how your staff respond to real-world lures, with click and report rates by team.
05
Your ISMS measured against ISO/IEC 27001:2022 so you know how far you are from a certification audit.
06
Controls mapped to the AICPA Trust Services Criteria, for SaaS teams selling to US or enterprise buyers.
Four steps, typically 2 to 6 weeks for a small or mid-sized business. Larger or multi-site scopes take longer and are agreed up front.
Step 1
A 30-minute call to agree systems, frameworks, testing and a fixed price.
Step 2
Documents, configurations and short interviews with your IT and leadership team.
Step 3
Penetration testing and phishing simulation, scheduled so business keeps running.
Step 4
Your audit report, a risk-ranked roadmap and a briefing for leadership.
Free 30-minute scoping call
Talk to Claude Pinto, Director at CyberSapiens Australia
Tell Claude what is driving the audit, whether that is an insurer, a tender or the board. You will leave with a clear scope, a timeline and a fixed-price quote within 24 hours.
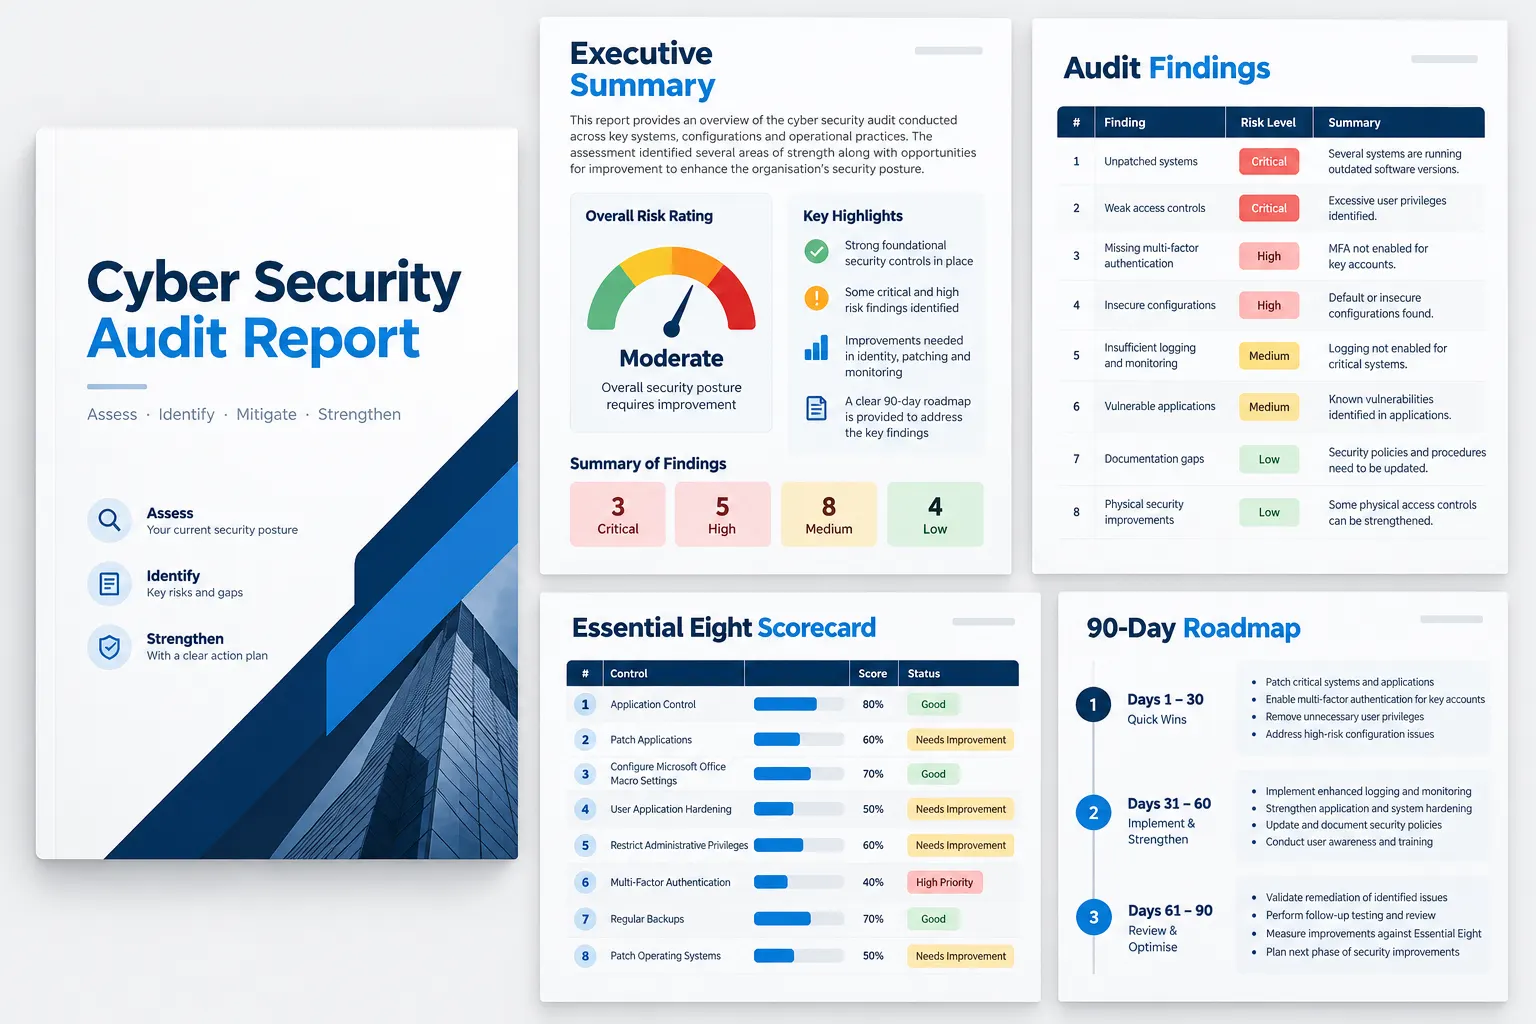
Your overall risk position on one page.
Critical, high, medium and low, each with evidence.
Current and target maturity for all eight strategies.
What could be exploited, and how staff responded.
Quick wins first, then the bigger projects in priority order.
Written for two audiences
Every finding comes with its risk rating, the evidence behind it and the fix, so your team or your IT provider can start straight away. Phishing results use the same reporting format as our PhishCare sample report.
You speak to senior people from the first call to the final walkthrough.

Lead Auditor, CyberSapiens Australia
Certified ISO 27001 Lead Auditor working with public, private and government clients across Australia, with experience across Essential Eight, ISO 27001, SOC 2, PCI DSS, NIST CSF, APRA CPS 234, VPDSS and the ISM.
Google review of CyberSapiens · ISO 27001 and SOC 2 Type II
"His detailed gap analysis and rigorous internal audit preparation ensured we were fully ready for the external audit."
Google review of CyberSapiens · SOC 2 Type II
"Claude and Ketki from Cyber Sapiens guided us seamlessly through our SOC 2 Type II journey."
The cost of a cyber security audit depends on what is in scope, not on a fixed menu. CyberSapiens quotes one fixed AUD price after a 30-minute scoping call, so there are no day-rate surprises.
Number of staff, sites and devices.
Essential Eight only, or ISO 27001 and SOC 2 as well.
Number of applications, networks and cloud accounts tested.
Number of users and campaigns included.
Get a fixed-price quote for your cyber security audit within 24 hours of your call.
Get your fixed quoteNot sure what to ask for? Start from the outcome you need.
| Type | What it answers | Best for |
|---|---|---|
| Cyber security audit | How secure are we overall, and what do we fix first? | Boards, insurers, a first independent review |
| Essential Eight assessment | What maturity level are we at today? | Government suppliers and Australian SMEs |
| Penetration test (VAPT) | Can an attacker actually break in? | Apps, cloud and networks before launch or audit |
| ISO 27001 certification | Do we run a certified information security system? | Tenders, enterprise and global customers |
| SOC 2 report | Can we prove our controls to US buyers? | SaaS companies selling to the US |
Already know you need a certification? See ISO 27001 certification in Australia or SOC 2 certification in Australia. Many clients start with an audit and use the findings as their certification roadmap.
Auditors look for these ten basics first. Count how many you can show evidence for today.
Fewer than seven? That is normal for a first audit, and exactly what the roadmap is for.
Ask any provider four questions: who will actually do the work, which framework they audit against, whether penetration testing and phishing are included or extra, and whether the price is fixed. A good audit ends with a plan you can act on, not just a list of problems.
CyberSapiens delivers audits remotely across Australia from our Port Melbourne office, with onsite work arranged when your scope needs it.
CyberSapiens Australia
Lvl 1, 206 Lorimer St, Port Melbourne VIC
1300 507 668 · sales@phishcare.com
30 minutes with Claude Pinto. Fixed-price quote within 24 hours. No obligation.
Prefer to talk now? Call 1300 507 668 or email sales@phishcare.com
The cost depends on your size, the frameworks in scope, how many systems are penetration tested and whether a phishing simulation is included. CyberSapiens provides a fixed-price quote within 24 hours of a free 30-minute scoping call.
A focused audit for a small or mid-sized business typically takes 2 to 6 weeks from kick-off to final report. Larger, multi-site or highly regulated scopes take longer and are agreed before work starts.
There is no general law requiring every business to have a cyber security audit. However, the Privacy Act requires reasonable steps to protect personal information, and insurers, government buyers and enterprise customers increasingly ask for independent evidence of your controls.
The terms are often used interchangeably. An assessment usually focuses on identifying risks and gaps, while an audit checks your controls against a defined standard and records the evidence. CyberSapiens audits include both, so you get the risk picture and the evidence.
No. A penetration test checks whether specific systems can be broken into. A cyber security audit is broader and also covers policies, access, backups, staff awareness and framework maturity. Penetration testing can be included as one part of the audit.
Yes, when it is in scope. Each of the eight ASD mitigation strategies is scored from Maturity Level 0 to 3, with the steps needed to reach your target level.
One fixed price, Lead Auditors from day one, and a plan your team can start on the week the report lands.
CyberSapiens Australia, Lvl 1 206 Lorimer St, Port Melbourne VIC · sales@phishcare.comStart your free trial now and strengthen your defense against phishing threats.
Train your employees, prevent attacks, and stay ahead of cybercriminals with our advanced phishing simulation.
PhishCare is a cutting-edge phishing simulation tool developed by CyberSapiens to help businesses enhance their cybersecurity defenses. By allowing organizations to conduct simulated phishing attacks, PhishCare enables them to evaluate employee susceptibility to phishing threats and implement targeted awareness training.
Copyright © 2025 PhishCare, LLC. All rights reserved.