SOC 2 Audit Readiness for Australian SaaS

SOC 2 Certification in Australia From Readiness to Report

Type 1 audit-ready in 6 to 8 weeks. Type 2 on a realistic 9 to 12 month plan. CyberSapiens Lead Auditors prepare you, a licensed CPA audit partner issues the report, and PhishCare keeps your awareness evidence running through the Type 2 period.

PhishCare is a product of CyberSapiens. SOC 2 readiness is delivered by CyberSapiens. Last updated .

  • 6 to 8 weeks

    to SOC 2 Type 1 readiness

  • AUD 8,000

    fixed price from, audit partner included

  • 1 team

    from gap assessment to signed report

  • 24 hours

    to your fixed-price quote

Do Australian companies need SOC 2?

No Australian law requires SOC 2, but US and enterprise customers increasingly do. Most Australian SaaS companies can be ready for a SOC 2 Type 1 audit in 6 to 8 weeks. Type 2 usually takes 9 to 12 months, because the auditor must see your controls working over time.

SOC 2 is an attestation, not a certificate: a licensed CPA firm issues a report under AICPA SOC 2 guidance. When buyers ask if you are "SOC 2 certified", they want that report.

Google review of CyberSapiens

"Claude and Ketki from Cyber Sapiens guided us seamlessly through our SOC 2 Type II journey… A big thank you for the end-to-end support through to CPA assessment."
Russell W · read on Google

Meet the people who will run your SOC 2

No hand-off to a junior team. The people you meet on the first call are the people who scope, prepare and stay with you through the CPA audit.

Claude Pinto, Director at CyberSapiens Australia

Claude Pinto

Director, CyberSapiens Australia

Claude has spent over 10 years helping Australian organisations across telecommunications, managed IT, cybersecurity, cloud and digital transformation turn technology into measurable business value.

Your first call: scope, Type 1 or Type 2 first, a realistic timeline and what SOC 2 will unlock commercially.

Claude Pinto on LinkedIn

Ketki Tidke, Lead Auditor at CyberSapiens Australia

Ketki Tidke

Lead Auditor, CyberSapiens Australia

Ketki specialises in governance, risk and compliance for public, private and government clients across Australia. She leads SOC 2 readiness and ISO 27001 projects at CyberSapiens, with further experience across PCI DSS, NIST CSF, Essential Eight, APRA CPS 234, VPDSS and the ISM.

Her role: gap assessment, controls and evidence, and audit-day support until your report is issued.

Ketki Tidke on LinkedIn
Who needs SOC 2 certification in Australia?

If two or more of these sound familiar, SOC 2 is probably already costing you deals.

  1. 01A US prospect has asked for your SOC 2 report
  2. 02Enterprise deals stall in vendor risk review
  3. 03Security questionnaires eat days every month
  4. 04You host or process customer data
  5. 05Investors raised security in due diligence
  6. 06You plan to sell into North America this year

It helps at home too: the controls tested in a SOC 2 audit are the same ones that reduce your risk under the OAIC's Notifiable Data Breaches scheme.

What's included in SOC 2 audit readiness

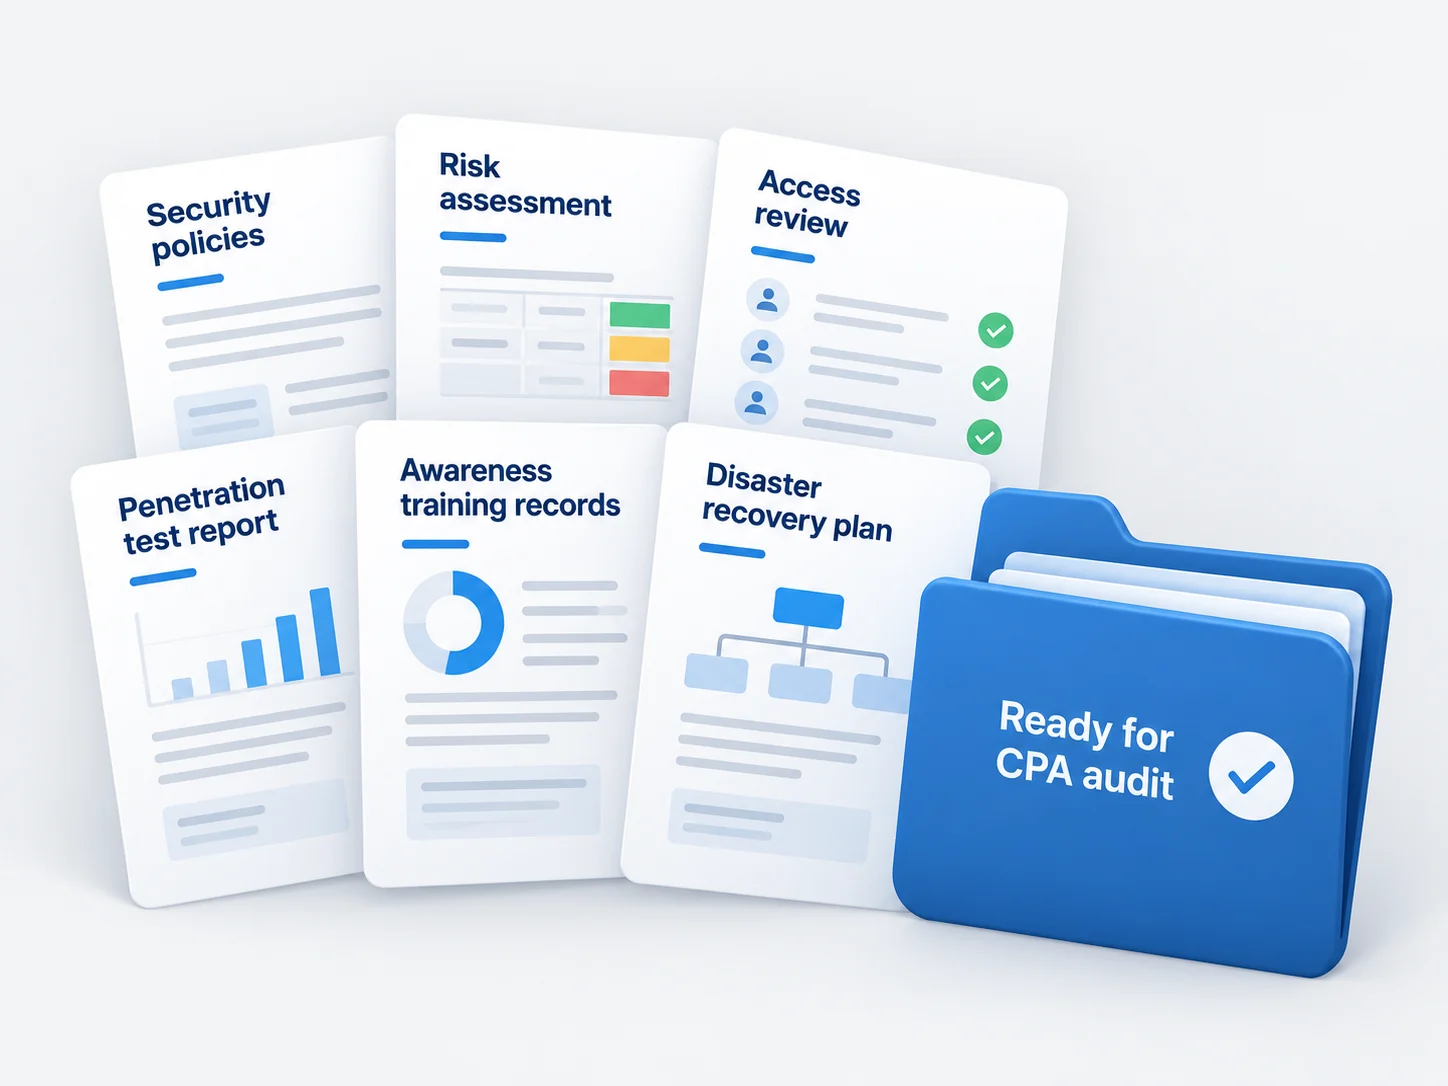
Illustration of the SOC 2 evidence pack CyberSapiens prepares: policies, risk assessment, access reviews, penetration test report, awareness training records and disaster recovery plan
  1. 01

    Gap assessment

    Scope, criteria and a prioritised gap list within weeks.

  2. 02

    Remediation and policies

    Policies written for you, access reviews, change management, logging and a tested DR plan.

  3. 03

    Penetration testing

    VAPT on your app and cloud, with a retest auditors can rely on.

  4. 04

    Awareness evidence with PhishCare

    Recurring phishing simulations and training with dated reports, an additional documentation boost auditors recognise as best practice.

  5. 05

    Audit coordination

    Evidence packs and fieldwork support with a licensed CPA audit partner until your report is issued.

The SOC 2 certification process and timeline

SOC 2 Type 1 typically takes 6 to 8 weeks. Type 2 typically takes 9 to 12 months from a standing start, because of the observation window.

  1. Step 1 · 4 to 8 weeks

    Readiness and gap analysis

    Scope, criteria, control mapping, gap list.

  2. Step 2 · 1 to 4 months

    Remediation

    Policies, tooling, access and change control, VAPT.

  3. Step 3 · 3 to 12 months

    Observation (Type 2 only)

    Controls run while evidence is collected.

  4. Step 4 · 4 to 8 weeks

    Audit and report

    The CPA audit partner tests evidence and issues your report.

A quick tip: any offer of a full Type 2 report in a few weeks is a red flag. Type 2 can never finish faster than its observation period plus fieldwork.

Know your SOC 2 timeline in 30 minutes

Talk to Claude Pinto and leave with a scope, a date and a fixed price.

Book a discovery call

SOC 2 readiness in practice

Case study · Sciative Solutions

How Sciative Solutions prepared for its SOC 2 audit

CyberSapiens helped Sciative Solutions, a technology and SaaS company, prepare for SOC 2 as part of its enterprise readiness strategy.

Download the Sciative case study (PDF)

"Moving from ad-hoc processes to a structured, compliance-driven operating model."

  • Risk assessment and remediation roadmap
  • Access control and change management formalised
  • Disaster recovery plan designed and documented
  • Evidence prepared for external audit
Start your SOC 2 readiness

SOC 2 certification cost in Australia: market vs fixed price

The audit fee is usually only 30 to 40 percent of real first-year SOC 2 spend. CyberSapiens quotes one fixed AUD price covering consultancy and the audit partner.

SOC 2 certification cost in Australia: typical market first-year cost versus CyberSapiens fixed price
Company profileTypical market, first year (USD)CyberSapiens, consultancy plus audit partner (AUD)
Early-stage startup
Security criteria only
20,000 to 50,0008,000 to 20,000
Small to mid-sized SaaS
20 to 50 staff, multiple criteria
60,000 to 150,00012,000 to 30,000
Large enterprise
Complex environment
150,000 to 250,000+30,000+

Price depends on criteria in scope, team and infrastructure size, existing controls and whether you need Type 1, Type 2 or both. Budget for a new Type 2 audit period each year.

Get your fixed quote

SOC 2 audit preparation checklist

How close are you? Most first-time companies already have four or five of these in place.

  1. Audit scope agreed
  2. Trust Services Criteria chosen
  3. Annual risk assessment recorded
  4. Security policies approved and signed
  5. MFA and quarterly access reviews
  6. Reviewed, approved code changes
  7. Central logging and vulnerability scans
  8. Vendor list with their SOC 2 reports
  9. Incident response plan tested
  10. Awareness training records for all staff

For item 10, PhishCare reports give auditors dated, per-employee evidence. See a sample PhishCare report

Choosing a SOC 2 auditor in Australia

Only a licensed CPA firm can audit and sign a SOC 2 report, and it must stay independent of whoever builds your controls. CyberSapiens prepares you and coordinates the audit with its licensed CPA partner, so you work with one team without compromising independence.

Comparing the market? Compare SOC 2 auditors and consultants in Australia or read our guide to SOC 2 compliance in Australia.

SOC 2 certification across Australia

  • Melbourne
    SaaS and health tech; our Port Melbourne base
  • Sydney
    Fintech and B2B software under bank vendor reviews
  • Brisbane
    Tech firms pairing SOC 2 with government expectations
  • Perth
    Resources tech selling to global operators

Book your SOC 2 discovery call

30 minutes with Claude Pinto. Fixed-price quote within 24 hours. No obligation.

Prefer to talk now? Call 1300 507 668

PhishCare Organic Contact Form

SOC 2 certification FAQs for Australian SaaS

How much does SOC 2 certification cost in Australia?

Typical first-year market spend is USD 20,000 to 50,000 for early-stage startups and USD 60,000 to 150,000 for small to mid-sized SaaS companies. CyberSapiens offers fixed prices covering consultancy and the audit partner from AUD 8,000 to 20,000 for startups and AUD 12,000 to 30,000 for small to mid-sized SaaS.

How long does SOC 2 certification take?

A SOC 2 Type 1 report typically takes 6 to 8 weeks. A Type 2 report from a standing start typically takes 9 to 12 months, including readiness, remediation, an observation period of 3 to 12 months and audit fieldwork.

Should we get SOC 2 Type 1 or Type 2 first?

If a deal is waiting, start with Type 1 to show your controls are designed correctly, then begin the Type 2 observation period straight away. If nothing is urgent, going directly to Type 2 avoids paying for two audits.

Who issues the SOC 2 report for an Australian company?

A licensed CPA firm performs the examination and signs the report under AICPA standards. Readiness consultants and compliance software help you prepare, but cannot issue the report.

Is SOC 2 required for Australian companies?

No Australian law requires SOC 2. It becomes necessary in practice when US or global enterprise customers make a current SOC 2 report a condition of doing business.

Can we do SOC 2 and ISO 27001 together?

Yes. Around 60 to 70 percent of the controls overlap, so one programme with shared policies and evidence is usually faster and cheaper. Read more about ISO 27001 certification in Australia.

Ready to get SOC 2 certified in Australia?

One fixed AUD price, Lead Auditors from day one, and a licensed CPA audit partner at the end.

CyberSapiens Australia, Lvl 1 206 Lorimer St, Port Melbourne, Australia · sales@phishcare.com