Cyber Security Audit Checklist for Australian Businesses
Last updated 14 October 2026 · Reviewed by Ketki Tidke, Certified ISO 27001 Lead Auditor, CyberSapiens · PhishCare is a product developed by CyberSapiens. Quick answer A cyber security audit checklist lists the controls an auditor will check: governance, assets, access, patching, hardening, backups, network and cloud, logging and incident response, suppliers, and staff awareness. […]
What Is a Human Firewall and How Do You Build One?
For decades, cybersecurity strategies focused primarily on technical defences. Firewalls, antivirus software, encryption systems, and intrusion detection tools were considered the backbone of organisational protection. While these technologies remain essential, attackers have increasingly shifted their focus towards the people who use them. Phishing emails, impersonation scams, business email compromise attacks, and social engineering tactics are […]
From Awareness to Action: How to Build a Reporting-First Security Culture
Cyber security awareness programs are common across organisations, yet employees do not always report suspicious emails. Without timely reporting, security teams lose valuable visibility and time when responding to potential threats. A reporting-first security culture moves beyond recognising phishing attacks to encouraging employees to take action. When suspicious messages are reported quickly, security teams can […]
How to Calculate ROI of Phishing Simulation Training
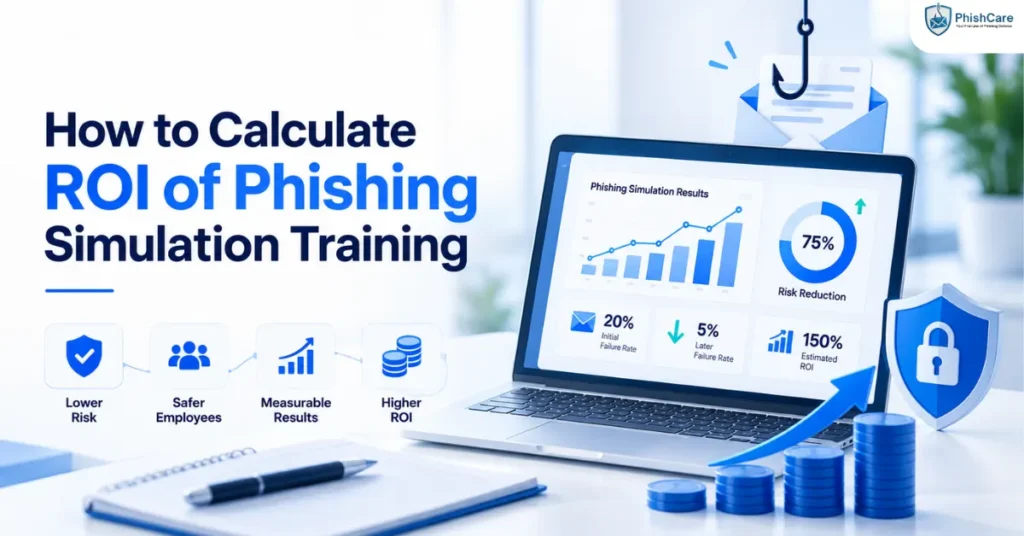
Organisations increasingly invest in phishing simulation training to strengthen employee awareness and reduce cyber risk. However, security leaders often face an important challenge when presenting these initiatives to executives: demonstrating measurable return on investment (ROI). Unlike traditional technology purchases, the value of security awareness programmes is not always immediately visible in financial terms. Phishing remains […]
The True Cost of a Single Phishing Click for Businesses
Phishing attacks remain one of the most effective cybercrime techniques targeting organisations today. While many businesses invest heavily in email security tools and network defences, attackers increasingly focus on exploiting human behaviour rather than technical vulnerabilities. A single phishing email that deceives an employee can trigger a chain of security incidents with serious financial and […]
How Security Awareness Training Reduces Cyber Insurance Premiums
Cyber insurance has become an essential component of modern risk management. As cyber attacks continue to increase in frequency and sophistication, organisations rely on cyber insurance policies to help mitigate the financial impact of data breaches, ransomware incidents, and operational disruptions. However, obtaining affordable cyber insurance coverage has become increasingly challenging in recent years. Insurance […]
Cybersecurity Training vs Data Breach Cost: A Business Comparison
Businesses today face an increasingly complex cyber threat landscape. From phishing attacks and credential theft to ransomware and business email compromise schemes, organisations across every industry are being targeted by cybercriminals. As a result, cyber security has become a critical priority for leadership teams seeking to protect sensitive data, financial assets, and operational continuity. Despite […]
How Board Members Evaluate Cyber Awareness Programs
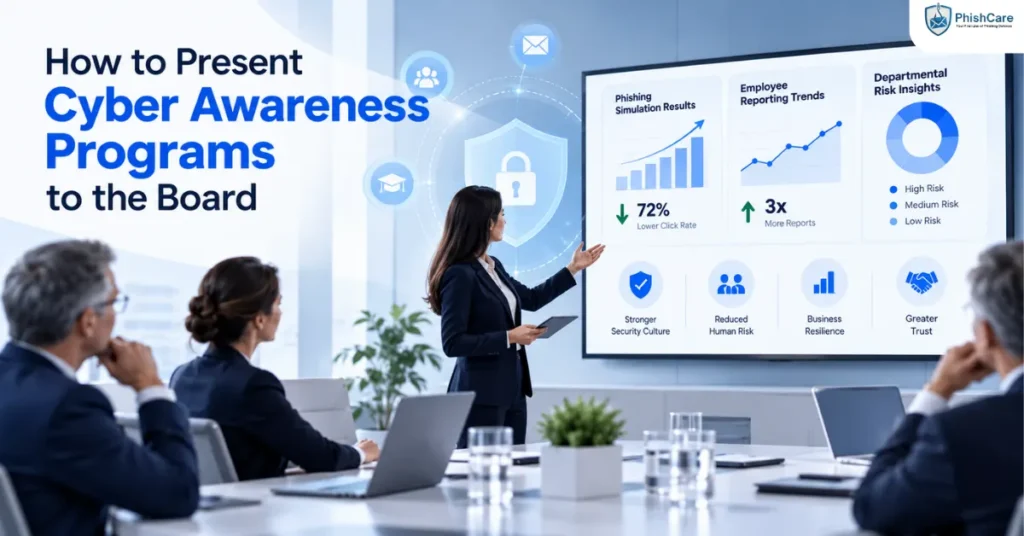
Cyber security is no longer viewed as a purely technical concern handled only by IT departments. In today’s threat landscape, cyber risk is a business risk that can affect financial stability, operational continuity, regulatory compliance, and organisational reputation. As a result, boards of directors are increasingly involved in overseeing cyber security strategies and evaluating how […]
Why Healthcare Staff Are Highly Targeted by Phishing Attacks
Healthcare organisations are among the most frequently targeted sectors in cyber attacks. Hospitals, clinics, insurance providers, and healthcare technology companies handle large volumes of sensitive patient information, financial data, and operational records. Because of this valuable data, attackers increasingly focus their efforts on healthcare environments. However, the primary reason healthcare institutions are targeted is not […]
Top 10 ISO 27001 Certification Consultants in Australia (2026 Guide)
Last updated 11 October 2026 Disclosure: PhishCare is a product developed by CyberSapiens, and CyberSapiens appears in this list. Our evaluation criteria are set out below so every provider is judged on the same basis. Information about other firms is summarised from their own public websites as of October 2026. Company names and trademarks belong […]