Cyber security awareness programs have evolved significantly over the past decade. What once consisted of annual compliance training sessions has transformed into a more strategic discipline focused on reducing human risk. Yet many organisations still struggle with a critical gap. They deliver training, but they do not measure whether behaviour is actually changing.
In 2026, phishing attacks remain one of the primary causes of data breaches worldwide. Attackers rely on social engineering tactics, impersonation, and psychological manipulation to bypass technical controls. Even with advanced email filtering and endpoint security in place, a single employee decision can expose sensitive systems and data. This reality has forced organisations to rethink how awareness programs are designed and evaluated.
Behavioral analytics has emerged as a foundational element of modern cyber security strategy. Instead of assuming that training equals preparedness, behavioural analytics examines how employees interact with real-world simulations and security scenarios. It measures patterns, identifies vulnerabilities, and provides actionable insight. Awareness without data is assumption. Awareness supported by behavioural analytics becomes measurable risk management. For organisations seeking to reduce phishing susceptibility and strengthen their human firewall, integrating behavioural data into awareness programs is no longer optional. It is essential.
What Is Behavioral Analytics in Cyber Security?
Behavioral analytics in cyber security refers to the systematic collection and analysis of data related to user actions, decisions, and interaction patterns. In the context of awareness programs, it focuses on how employees respond to simulated phishing attacks, suspicious emails, and security prompts.
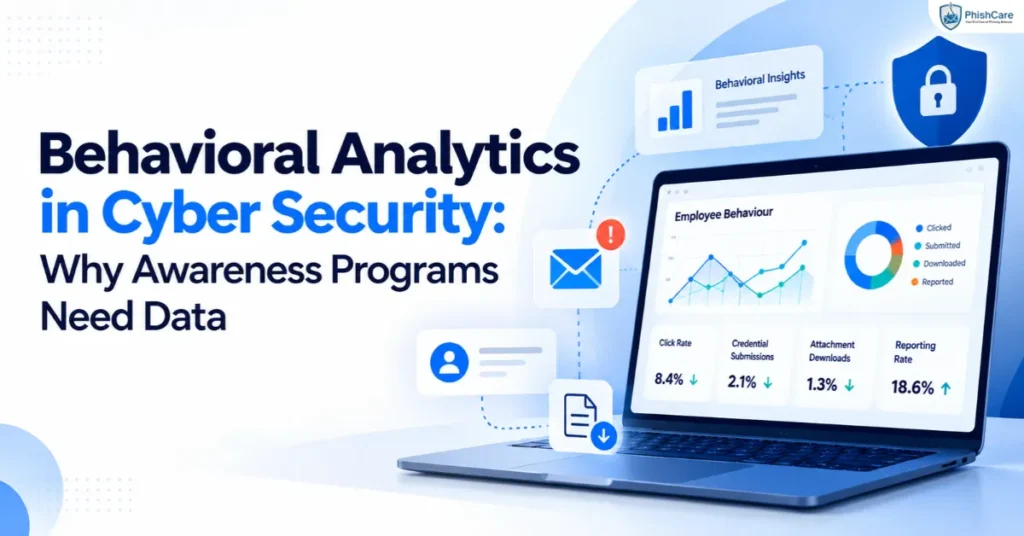
Rather than evaluating knowledge through quizzes alone, behavioural analytics measures real behaviour under realistic conditions. It tracks actions such as clicking links, submitting credentials, downloading attachments, and reporting suspicious messages. This data provides a more accurate representation of organisational vulnerability than training completion metrics.
Key areas of behavioural analysis
User actions
Clicking links, submitting credentials, and downloading attachments.
Decision patterns
How employees respond to simulated phishing attacks and security prompts.
Reporting behaviour
Whether employees identify and report suspicious messages.
Why Traditional Awareness Metrics Are Insufficient
Many awareness programs rely on surface-level indicators such as course completion rates or test scores. While these metrics demonstrate participation, they do not reflect how employees behave when confronted with real threats.
An employee may score highly on a training assessment yet still click on a convincing phishing email during a busy workday. Knowledge does not always translate into action.
Knowledge does not always translate into action.
Behavioral analytics addresses this disconnect by focusing on observable behaviour. It evaluates how employees act in realistic scenarios, providing insight into decision-making under pressure. Without behavioural data, organisations cannot accurately determine whether their awareness investments are producing measurable improvement.
These challenges become more significant as generative AI changes phishing attacks in 2026, making it important to assess actual employee responses rather than relying on training completion metrics alone.
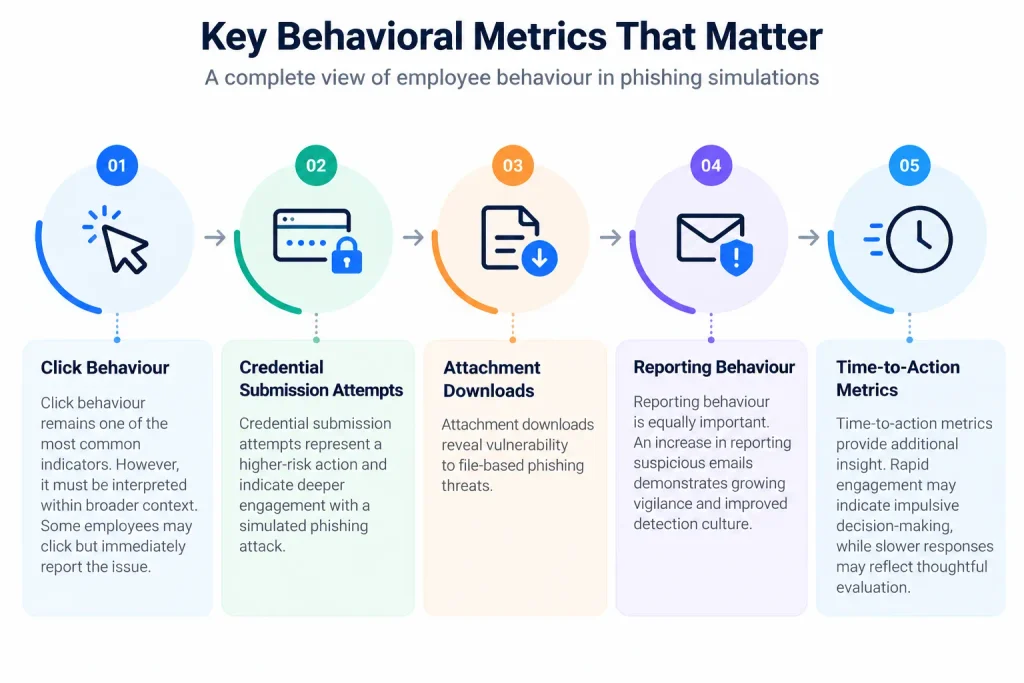
Key Behavioral Metrics That Matter
Effective behavioural analytics in awareness programs typically evaluates multiple dimensions of employee interaction.
01
Click Behaviour
Click behaviour remains one of the most common indicators. However, it must be interpreted within broader context. Some employees may click but immediately report the issue.
02
Credential Submission Attempts
Credential submission attempts represent a higher-risk action and indicate deeper engagement with a simulated phishing attack.
03
Attachment Downloads
Attachment downloads reveal vulnerability to file-based phishing threats.
04
Reporting Behaviour
Reporting behaviour is equally important. An increase in reporting suspicious emails demonstrates growing vigilance and improved detection culture.
05
Time-to-Action Metrics
Time-to-action metrics provide additional insight. Rapid engagement may indicate impulsive decision-making, while slower responses may reflect thoughtful evaluation.
By combining these metrics, organisations develop a comprehensive view of behavioural risk rather than relying on a single data point.
Turning Data Into Strategic Insight
Collecting behavioural data is only the first step. The true value lies in interpretation and action. Organisations should analyse trends over time to identify whether click rates are decreasing, reporting rates are increasing, and high-risk patterns are diminishing. Departments or roles that consistently demonstrate higher risk may require targeted reinforcement.
What organisations should monitor
Click rates
Identify whether click rates are decreasing over time.
Reporting rates
Track whether employees are reporting more suspicious messages.
High-risk patterns
Identify departments or roles that may require targeted reinforcement.
Executive-level visibility is also critical. When behavioural analytics is presented in structured dashboards, leadership gains insight into human-related cyber risk as part of broader enterprise risk discussions. This data-driven approach transforms awareness programs from compliance exercises into strategic security initiatives. Organisations can also explore how board members evaluate cyber awareness programs to understand the importance of leadership visibility.
The Role of Continuous Simulation
Behavioral analytics is most effective when paired with continuous phishing simulation. A single annual test provides limited insight. Threat actors constantly evolve their tactics, and employee behaviour must adapt accordingly.
Ongoing simulation campaigns create multiple data points throughout the year. This allows organisations to observe improvement trends, identify regression, and adjust training strategies accordingly. Continuous exposure builds habit and instinct. Repetition strengthens recognition of suspicious patterns and reinforces secure decision-making.
Continuous Simulation. Measurable Behaviour.
01. Observe
Collect behavioural data across simulation campaigns.
02. Evaluate
Identify improvement trends and behavioural regression.
03. Adapt
Adjust training strategies to reinforce secure decisions.
Organisations can also explore how to calculate the ROI of phishing simulation training when evaluating their awareness initiatives.
Avoiding Misuse of Behavioural Data
While behavioural analytics is powerful, it must be implemented responsibly. Risk scores and interaction metrics should not be used to shame employees or create a punitive environment. A blame-driven culture discourages reporting and reduces transparency. The objective of behavioural analytics is improvement, not punishment.
Improvement, Not Punishment
Organisations should communicate clearly that simulations are learning tools designed to strengthen collective resilience. When employees understand the purpose, participation becomes more constructive and effective.
PhishCare: Data-Driven Awareness Through Behavioral Analytics
PhishCare integrates behavioural analytics into its phishing simulation framework to support measurable Human Risk Management. The platform captures detailed interaction data, including link clicks, credential submissions, attachment downloads, and reporting behaviour. Rather than presenting isolated metrics, PhishCare enables organisations to analyse trends across departments and roles, identifying persistent vulnerabilities and areas of improvement.
Immediate feedback delivered at the moment of interaction reinforces learning while generating behavioural data points. Continuous simulation campaigns provide longitudinal insight into employee risk patterns.
By combining realistic attack scenarios with structured analytics dashboards, PhishCare helps organisations move from awareness assumptions to data-driven decision-making. This approach strengthens the human firewall while aligning awareness initiatives with measurable risk reduction objectives.
From Awareness to Data-Driven Decisions
Interaction data
Capture employee responses to simulated phishing attacks.
Trend analysis
Analyse patterns across departments and roles.
Learning feedback
Reinforce learning at the moment of interaction.
The Future of Awareness Programs Is Data-Centric
As cyber threats continue to evolve, awareness programs must evolve as well. Delivering training without measurement is no longer sufficient. Organisations require visibility into behavioural risk, measurable improvement, and executive-level reporting. Behavioral analytics provides the foundation for this transformation. It enables security teams to understand not just what employees know, but how they act.
A Data-Centric Approach to Awareness
Continuous Simulation
Observe employee behaviour across ongoing simulations.
Behavioural Insight
Understand how employees respond to security scenarios.
Structured Reporting
Provide visibility into behavioural risk and improvement.
In 2026 and beyond, the most effective cyber security awareness programs will be those that integrate continuous simulation, behavioural insight, and structured reporting into a cohesive Human Risk Management strategy. Data is no longer optional. It is the future of awareness.
Frequently Asked Questions
1. What is behavioral analytics in cyber security?
Behavioral analytics in cyber security involves analysing user interaction patterns to identify vulnerabilities and measure how employees respond to phishing and social engineering attempts.
2. Why do awareness programs need behavioral data?
Behavioral data reveals whether training is influencing real-world decisions. Without data, organisations cannot measure improvement or identify high-risk patterns.
3. Is click rate enough to evaluate phishing risk?
No. Click rate is only one indicator. A comprehensive evaluation should include credential submissions, reporting behaviour, time-to-action metrics, and trend analysis.
4. How often should behavioural analytics be reviewed?
Behavioural metrics should be reviewed continuously through ongoing simulation campaigns rather than relying on annual assessments.
5. Can behavioural analytics reduce phishing incidents?
Yes. When used responsibly, behavioural analytics helps organisations identify weaknesses, reinforce learning, and reduce susceptibility to phishing over time.
Content Reviewed By
Mohammed Nawaz Sajjad
Sr. Security Analyst at CyberSapiens | Phishing Simulation | Ethical Hacker | Bug Hunter | Red Team
Nawaz is a practising security analyst specializing in phishing simulation campaigns, employee awareness assessments, red team exercises, and ethical hacking.
He leads phishing simulation deployments at PhishCare, a product developed by CyberSapiens, with hands-on experience evaluating and deploying phishing simulation tools across organizations in multiple industries and regions globally.
View LinkedIn ProfileTurn Awareness Into Measurable Risk Reduction
Strengthen your human firewall with data-driven phishing simulations and behavioural insights from PhishCare.
Contact PhishCare