Phishing attacks remain one of the most effective cybercrime techniques targeting organisations today. While many businesses invest heavily in email security tools and network defences, attackers increasingly focus on exploiting human behaviour rather than technical vulnerabilities. A single phishing email that deceives an employee can trigger a chain of security incidents with serious financial and operational consequences.
For many organisations, the idea that one click could lead to significant damage may seem exaggerated. However, phishing attacks often begin with a simple action: an employee clicking a malicious link, downloading a deceptive attachment, or entering credentials into a fraudulent login page. Learning how phishing works and why it succeeds helps businesses understand how these seemingly minor actions can expose critical systems.
Once attackers gain access, they may move laterally through systems, impersonate employees, steal sensitive data, and initiate fraudulent transactions. What begins as a moment of human error can escalate into a cyber incident affecting multiple departments, customers, and business partners.
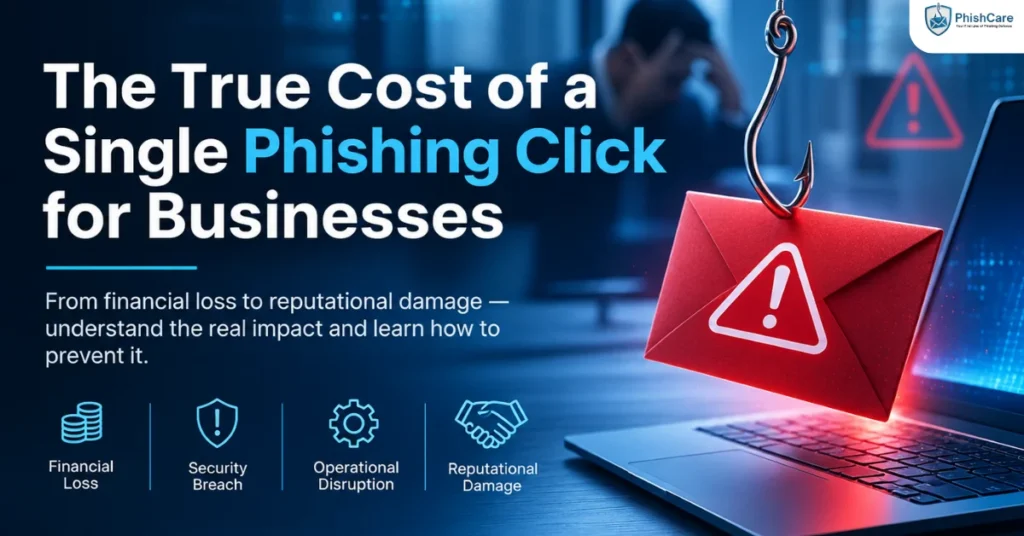
Understanding the true cost of a phishing click means looking beyond the immediate technical impact. Businesses must consider financial losses, operational disruption, regulatory exposure, reputational damage, and the long-term consequences of compromised trust.
One Click Can Trigger a Chain of Consequences
A successful phishing attempt can lead to credential theft, fraudulent payments, data exposure, system downtime, and costly incident response. Strengthening employee awareness is an important part of reducing these risks before a real attack succeeds.
Financial Loss and Fraud
One of the most direct consequences of phishing attacks is financial loss. Attackers frequently use deceptive emails to impersonate executives, vendors, or financial institutions, requesting urgent payments or redirecting legitimate transactions. These messages often rely on urgency and familiarity to pressure employees into acting before verifying the request.
These attacks, often referred to as business email compromise (BEC), can result in substantial fraudulent transfers. Employees who believe they are responding to legitimate instructions may unknowingly send funds to criminal accounts. Similar tactics can also expose payment details or sensitive financial information.
Fraudulent Transfers
Employees may unknowingly authorise payments to attacker-controlled accounts after receiving convincing impersonation emails.
Investigation Costs
Businesses may need forensic analysis, legal advice, transaction reviews, and additional incident response support.
Recovery Expenses
Recovering from fraud may involve additional administrative work, financial reconciliation, and efforts to restore normal operations.
Even when some funds are recovered, the investigation and remediation process can create additional expenses and consume valuable employee time. Recovery is not guaranteed, and the final impact depends on the incident’s circumstances.
Prevention Starts With Verification
Establish clear procedures for verifying payment changes, unusual financial requests, and executive instructions through a separate trusted communication channel. Regular phishing awareness training can help employees recognise manipulation tactics before money is transferred.
Credential Theft and System Access
Many phishing emails are designed to steal employee login credentials. Attackers create convincing replicas of legitimate login portals for cloud services, email platforms, and internal applications. Employees may be tricked into entering their usernames, passwords, or other sensitive authentication details without realising the page is fraudulent.
When credentials are captured, attackers may use them to access corporate systems, read confidential communications, or reach sensitive business information. Valid credentials can make malicious activity harder to distinguish from legitimate user behaviour, particularly when additional safeguards are not in place.
Fake Login Pages
Fraudulent websites imitate trusted services to trick employees into revealing their login credentials.
Unauthorised Access
Stolen credentials may let attackers access email accounts, cloud platforms, and internal business applications.
Further Attacks
Compromised accounts can become a starting point for data theft, internal impersonation, or malware deployment.
Credential theft can therefore become the first stage of a more complex cyberattack, including ransomware or data exfiltration. The eventual impact depends on the level of access obtained, the protections in place, and how quickly the incident is detected.
Help Employees Recognise Fake Login Pages
Train employees to inspect website addresses, question unexpected login requests, and avoid entering credentials through links in suspicious emails. Use multi-factor authentication and report unusual account activity promptly.
Learn how to spot a fake login page →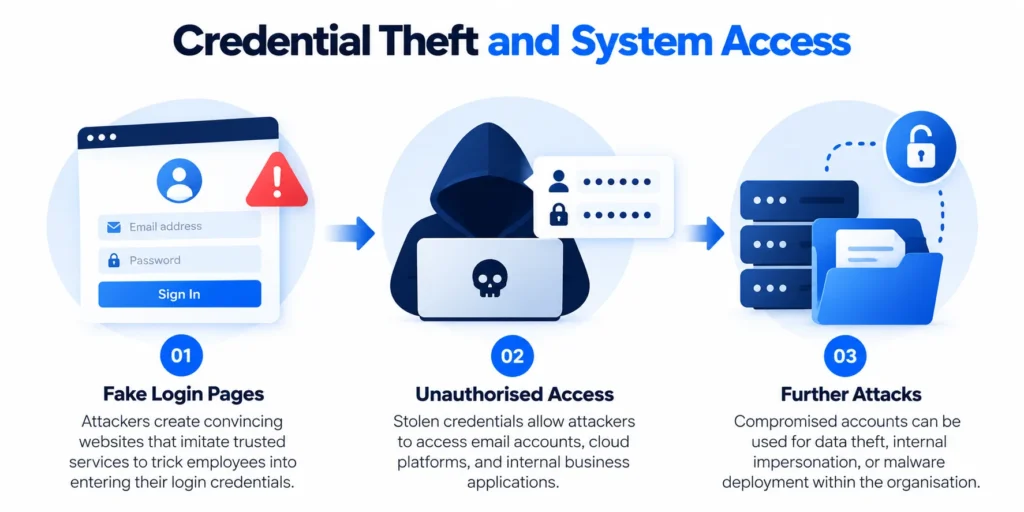
Operational Disruption
A phishing attack that compromises accounts or systems can disrupt normal business operations. Security teams may need to disable affected accounts, isolate network segments, or temporarily shut down systems to contain the threat. While these actions help limit further damage, they can interrupt everyday business activities.
The impact can extend across departments. Employees may lose access to essential applications, customer-facing services may become unavailable, and time-sensitive projects may be delayed. In severe cases, organisations may experience prolonged downtime while investigating the incident and restoring affected systems.
Interrupted Workflows
Employees may be unable to access email, business applications, or shared resources needed to complete routine tasks.
Service Downtime
Affected systems may need to be isolated or restored, potentially delaying customer services and critical operations.
Recovery Workload
IT and security teams must investigate the incident, reset credentials, review activity, and help restore normal operations.
The longer an incident remains undetected or unresolved, the greater its potential operational impact. Recovery can also divert security and IT professionals from planned projects, maintenance, and other essential responsibilities.
Reduce Disruption Before an Attack Escalates
Establish a clear process for reporting suspicious emails, responding to compromised accounts, and escalating potential incidents. Regular employee awareness training can help staff identify phishing attempts and report them promptly, giving security teams an opportunity to respond earlier.
Regulatory and Legal Consequences
Organisations that handle sensitive customer, employee, or financial information may face regulatory scrutiny when a phishing attack leads to a data breach. Data protection laws and industry regulations can require businesses to implement appropriate safeguards and report certain incidents to the relevant authorities.
If attackers gain access to personal or confidential information, an organisation may need to investigate the incident, assess its impact, notify affected parties where required, and implement corrective measures. Depending on the circumstances and applicable requirements, the incident may also result in regulatory penalties or legal claims from affected customers and business partners.
Regulatory Scrutiny
Authorities may examine how the organisation protected sensitive information and responded to the incident.
Legal Exposure
Affected customers, partners, or other parties may pursue legal remedies depending on the facts and applicable law.
Remediation Costs
Businesses may need additional security controls, incident reporting processes, and corrective measures to address identified weaknesses.
These consequences can extend the cost of a phishing incident beyond immediate technical recovery. Organisations should understand the regulatory obligations relevant to their industry, location, and data processing activities rather than assuming that every incident triggers the same requirements.
Make Security Awareness Part of Risk Management
Employee training, clear incident-reporting procedures, access controls, and regular security reviews can help organisations strengthen their safeguards. Awareness training is one part of a broader security programme, not a guarantee against regulatory or legal consequences.
Reputational Damage
Reputation is one of the most valuable assets an organisation can have. When customers, employees, or business partners learn that a company has experienced a cyber incident, their confidence in its ability to protect sensitive information may decline. Even when the initial attack begins with a single phishing email, the resulting loss of trust can affect business relationships long after systems have been restored.
The impact can be particularly serious when an incident exposes customer information, disrupts essential services, or reveals weaknesses in internal security practices. Understanding how phishing attacks work helps organisations recognise the social engineering techniques that can put both business operations and customer trust at risk.
Customer Confidence
Customers may reconsider their relationship with a business if they believe their personal or financial information is not adequately protected.
Business Relationships
Partners and suppliers may reassess the risks of working with an organisation following a security incident.
Market Perception
Publicly reported incidents can influence brand perception, customer retention, and future business opportunities.
Rebuilding trust often requires transparent communication, effective incident management, and sustained investment in stronger security practices. Organisations must also demonstrate that they are addressing the weaknesses that contributed to the incident rather than relying on short-term fixes.
Build a Security-Aware Workforce
Employees who can recognise suspicious messages and report them promptly can help organisations respond before a potential threat escalates. Explore how PhishCare phishing simulations can support ongoing awareness initiatives and help security teams identify areas where additional training may be needed.
Explore PhishCareRecovery and Incident Response Costs
Responding to a phishing incident requires coordination between security, IT, legal, and business teams. Once suspicious activity is identified, organisations must investigate how the attack occurred, determine which systems or accounts were affected, and take steps to contain the threat. These activities require time, expertise, and financial resources.
Depending on the severity of the incident, businesses may need to reset compromised credentials, restore affected systems, review access logs, and assess whether sensitive information was exposed. External cybersecurity consultants or digital forensic investigators may also be required to support the response.
Investigation
Security teams examine email activity, access logs, affected accounts, and potential indicators of compromise to establish the incident’s scope.
Containment and Recovery
Teams secure compromised accounts, remove malicious access, restore affected systems, and verify that business operations can resume safely.
Remediation
Organisations address security weaknesses, improve monitoring, update procedures, and provide additional employee training where needed.
Even incidents that do not cause major data loss can consume significant organisational effort. Time spent on emergency response may delay planned projects, increase operational expenses, and require additional security investments. The overall cost depends on the attack’s scope, the organisation’s preparedness, and how quickly the incident is contained.
Prevention Can Reduce Recovery Burden
Strong technical controls, clear incident-reporting procedures, and regular employee awareness activities can help organisations identify phishing attempts earlier. PhishCare supports awareness programmes through phishing simulations that help employees practise recognising suspicious messages and give security teams insights into training needs.
Explore PhishCarePreventing the Cost of Phishing Through Awareness
Because phishing attacks frequently exploit human behaviour, prevention must go beyond email filters and technical security controls. Employees need to recognise suspicious messages, question unexpected requests, and understand how seemingly routine actions can expose organisational systems and data.
Regular security awareness training helps employees identify common phishing indicators, including unusual sender addresses, urgent payment requests, suspicious links, unexpected attachments, and requests for sensitive information. Reinforcing these skills can help reduce the likelihood that an employee unknowingly interacts with a malicious message.
Recognise Warning Signs
Teach employees to inspect links, verify sender identities, question unexpected attachments, and recognise pressure tactics commonly used in phishing.
Verify Before Acting
Encourage employees to confirm payment changes, credential requests, and sensitive transactions through a separate, trusted communication channel.
Report Suspicious Activity
Provide a simple reporting process so employees can alert security teams quickly when they receive or interact with a suspicious message.
Awareness programmes become more useful when training is reinforced through realistic practice. Phishing simulations allow employees to experience controlled scenarios that reflect common attack techniques. The results can help security teams identify knowledge gaps, tailor training, and monitor changes in employee behaviour over time.
Turn Awareness Into Everyday Security Habits
Consistent training, realistic practice, and clear reporting procedures help employees build safer habits. Reviewing simulation results and addressing recurring mistakes can help organisations strengthen awareness and reduce the risk of phishing-related incidents.
Strengthening Employee Awareness With PhishCare
Reducing the cost of phishing incidents requires continuous reinforcement of employee awareness. Traditional training can introduce common threats, but employees also need opportunities to practise identifying suspicious messages in realistic scenarios. Regular simulations and targeted learning can help organisations turn security knowledge into everyday behaviour.
Phishing simulation programmes help organisations assess how employees respond to deceptive emails, including impersonation attempts, urgent financial requests, and routine-looking business communications. These controlled exercises can reveal where additional guidance may be needed before employees encounter similar tactics in real attacks.
Realistic Simulations
Use controlled phishing scenarios to help employees practise identifying suspicious links, deceptive requests, and sender impersonation.
Immediate Learning
Provide timely feedback after a simulated interaction so employees can understand the warning signs they may have missed.
Behavioural Insights
Review participation, reporting behaviour, and recurring mistakes to identify teams or topics that may need additional training.
Measuring programme outcomes helps security teams understand whether awareness initiatives are improving employee responses over time. Useful indicators include phishing reporting rates, interaction rates during simulations, repeat mistakes, and the time taken to report suspicious messages.
Make Awareness Measurable
Use simulation results to refine training, address recurring weaknesses, and track progress over time. Consistent measurement can help organisations make informed decisions about their security awareness programmes and demonstrate ongoing efforts to reduce human-related cyber risk.
The Real Cost of a Phishing Click
A phishing attack rarely ends with a single action. What begins as a simple click can escalate into financial loss, system compromise, regulatory scrutiny, operational disruption, and reputational harm. The overall impact depends on the attack, the information or systems affected, and how quickly the organisation responds.
Organisations that recognise the full scope of these risks are better positioned to invest in preventive measures. Email security, strong authentication, access controls, clear reporting procedures, and regular employee awareness training all contribute to a more resilient security environment.
Prevent
Strengthen email security, authentication, and employee awareness to reduce exposure to phishing attempts.
Detect
Encourage employees to report suspicious messages and help security teams identify potential incidents early.
Respond
Maintain clear incident response procedures to contain threats, investigate suspicious activity, and restore affected systems.
Preventing the first click is important, but organisations must also prepare to respond when security controls are bypassed. Combining employee awareness with effective technical safeguards and incident response planning helps reduce the likelihood that a phishing attempt becomes a costly business incident.
Final Takeaway
One Click Can Cost More Than You Expect
Building a security-aware workforce, encouraging prompt reporting, and maintaining strong technical controls can help organisations reduce phishing risks and protect their financial, operational, and reputational assets.
Frequently Asked Questions About Phishing Attacks
Find answers to common questions about phishing risks, their business impact, and ways to prevent costly security incidents.
1. Why is a single phishing click so dangerous?
A phishing click can expose employees to credential theft, malware, or fraudulent websites. If attackers gain access to corporate accounts or systems, the incident can escalate into data theft, financial fraud, or operational disruption.
2. What is the average cost of a phishing attack?
There is no single cost that applies to every phishing attack. The financial impact depends on the severity of the incident and may include fraudulent payments, investigation expenses, system recovery, legal costs, regulatory consequences, and reputational damage.
3. Can phishing attacks bypass email security tools?
Yes. Some phishing emails use convincing social engineering, compromised legitimate accounts, or deceptive links that evade automated detection. Email security tools are important, but they should be combined with employee awareness, strong authentication, and clear reporting procedures.
4. How can businesses reduce phishing risk?
Businesses can reduce phishing risk through regular security awareness training, phishing simulations, multi-factor authentication, secure email controls, payment verification procedures, and prompt reporting of suspicious activity.
5. Why is employee awareness important in preventing phishing?
Phishing attacks often target human behaviour rather than technical weaknesses alone. Employees who recognise suspicious messages, verify unusual requests, and report potential threats promptly can help security teams intervene before an incident escalates.
About the Author
Mohammed Nawaz Sajjad
Mohammed Nawaz Sajjad writes about cybersecurity, phishing threats, security awareness, and practical strategies organisations can use to strengthen their security posture.
Connect on LinkedIn →