For decades, cybersecurity strategies focused primarily on technical defences. Firewalls, antivirus software, encryption systems, and intrusion detection tools were considered the backbone of organisational protection. While these technologies remain essential, attackers have increasingly shifted their focus towards the people who use them.
Phishing emails, impersonation scams, business email compromise attacks, and social engineering tactics are designed to manipulate human behaviour rather than exploit technical flaws. A single click on a malicious link, an impulsive response to an urgent request, or misplaced trust can bypass even advanced security infrastructure.
What Is a Human Firewall?
A human firewall is a workforce that can recognise suspicious activity, question unusual requests, and report potential cyber threats. Instead of unintentionally becoming an entry point for attackers, employees become an active layer of organisational defence.
Building a human firewall is not about blaming employees for security mistakes. It is about giving them the knowledge, practical experience, and confidence to identify suspicious activity and respond appropriately. Regular awareness training, realistic phishing simulations, clear reporting procedures, and supportive leadership help turn security knowledge into everyday behaviour.
As cyber threats evolve, organisations need people and technology to work together. A strong human firewall complements technical security controls by helping employees make safer decisions, recognise potential attacks, and contribute to a more resilient security culture.
Why a Human Firewall Matters More Than Ever
In 2026, phishing attacks are increasingly sophisticated. Attackers use artificial intelligence to create convincing messages, impersonate executives, and imitate routine business processes. Some attacks originate from compromised accounts or trusted platforms, making them more difficult to identify through technical filtering alone. Understanding how generative AI is changing phishing attacks in 2026 helps organisations recognise why employees need practical, ongoing security awareness.
Remote and hybrid work environments have also expanded the attack surface. Employees access corporate systems from different locations, networks, and devices. This creates additional opportunities for attackers to exploit weak verification practices, distracted decision-making, and gaps in communication. Businesses can better understand these challenges by exploring phishing threats in remote work environments.
The Human Factor in Cybersecurity
Attackers often exploit urgency, authority, familiarity, and trust to influence employee decisions. A convincing payment request or an unexpected message from someone appearing to be a senior executive can prompt action before the recipient verifies its authenticity. A well-trained workforce helps interrupt this pattern by questioning unusual requests, confirming identities, and reporting suspicious activity.
A human firewall does not replace firewalls, endpoint protection, multi-factor authentication, or other technical controls. Instead, it adds a behavioural layer of defence. Employees who know how to identify warning signs and follow established reporting procedures can help organisations respond earlier and limit the potential impact of an attack.
The goal is to make secure behaviour part of everyday work. When employees receive regular training, practise recognising realistic threats, and feel confident reporting mistakes, they become active participants in protecting organisational systems, sensitive information, and business operations.
Core Elements of a Strong Human Firewall
Building a human firewall requires more than distributing security policies or conducting occasional awareness sessions. Organisations need a structured approach that combines continuous learning, practical experience, clear reporting procedures, and leadership support. The objective is to help employees apply secure behaviours consistently in their daily work.
01
Continuous Security Awareness Training
Employees need regular guidance on evolving threats, including phishing, impersonation, and social engineering. Training should be practical and relevant to everyday business workflows, helping employees recognise warning signs and make safer decisions.
02
Realistic Phishing Simulation
Simulated phishing campaigns allow employees to encounter realistic attack scenarios in a controlled environment. These exercises help reinforce recognition skills and provide opportunities to learn from mistakes without exposing real organisational systems to the simulated threat.
03
Clear Reporting Processes
Employees should know exactly how and where to report suspicious emails, unusual requests, and potential security incidents. A simple, accessible reporting process helps reduce hesitation and enables security teams to investigate potential threats sooner.
04
A Non-Punitive Security Culture
Fear of blame can discourage employees from reporting mistakes or suspicious activity. A supportive environment encourages prompt disclosure, constructive feedback, and learning. The focus should be on improving security behaviour rather than discouraging people from speaking up.
05
Leadership Involvement
Security awareness becomes more effective when leaders demonstrate responsible behaviour and reinforce verification procedures. Clear support from management helps establish security as a shared organisational responsibility rather than a task belonging only to the IT team.
Connect Awareness With Measurable Behaviour
An effective human firewall combines employee education with practical exercises and measurable outcomes. Organisations can strengthen this approach by understanding how board members evaluate cyber awareness programs, including the importance of tracking progress, identifying risks, and communicating security improvements.
How to Build a Human Firewall Step by Step
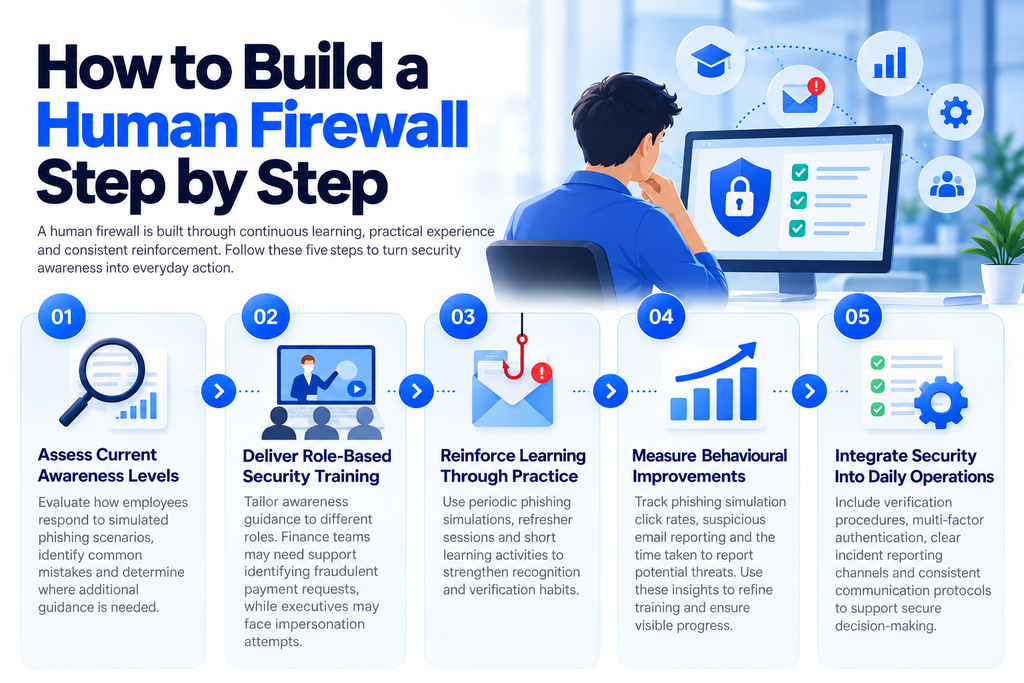
Building a human firewall is a strategic process rather than a one-time initiative. Organisations need to understand current employee behaviour, provide relevant training, reinforce secure habits, and measure progress over time. The following steps help turn security awareness into consistent action.
Assess Current Awareness Levels
Evaluate how employees respond to simulated phishing scenarios, identify common mistakes, and determine where additional guidance is needed. Use the findings to establish a baseline for measuring future improvements.
Deliver Role-Based Security Training
Tailor awareness guidance to employee responsibilities and exposure to risk. Finance teams may need additional support identifying fraudulent payment requests, while executives may face impersonation attempts and targeted business email compromise attacks.
Reinforce Learning Through Practice
Use periodic phishing simulations, refresher sessions, and short learning activities to reinforce recognition and verification habits. Repeated practice helps employees apply what they learn when suspicious messages appear in real work situations.
Measure Behavioural Improvements
Track trends such as phishing simulation click rates, suspicious email reporting, and the time taken to report potential threats. Use these indicators to identify gaps, refine training, and assess whether employee behaviour is improving.
Integrate Security Into Daily Operations
Make secure decisions part of routine workflows. Verification procedures for financial transactions, multi-factor authentication, clear incident reporting channels, and consistent communication protocols help employees follow safer practices without relying on memory alone.
Make Training a Business Investment
A structured human firewall programme should focus on measurable risk reduction rather than training completion alone. Organisations can also explore the relationship between cybersecurity training and the potential cost of a data breach when evaluating awareness initiatives and prioritising security investments.
Common Mistakes When Building a Human Firewall
Many organisations invest in security awareness but struggle to turn that investment into lasting behavioural change. Treating training as a one-time activity, overlooking employee concerns, or measuring only limited indicators can weaken a human firewall. Recognising these mistakes helps organisations build a more effective and sustainable security culture.
Mistake 01
Treating Awareness as a Checkbox
When security awareness is viewed only as an administrative task, employees may complete training without applying its lessons. Effective programmes focus on practical decision-making, threat recognition, and everyday security behaviour.
Mistake 02
Relying on One-Time Training
A single training session cannot keep employees prepared for constantly evolving phishing and social engineering tactics. Without regular reinforcement, employees may forget warning signs and return to familiar habits.
Mistake 03
Focusing Only on Click Rates
Phishing simulation click rates provide useful information, but they do not show the full picture. Organisations should also consider reporting rates, response times, repeated behavioural patterns, and whether employees follow verification procedures.
Mistake 04
Creating a Fear-Based Culture
Employees who fear embarrassment or punishment may hesitate to report suspicious messages or admit mistakes. A supportive environment encourages early reporting and gives security teams a better opportunity to investigate potential incidents.
Build a Culture of Continuous Improvement
A mature human firewall strategy combines regular learning, realistic practice, supportive reporting procedures, and meaningful performance measurement. Organisations can evaluate the business value of these initiatives by understanding how to calculate the return on investment of phishing simulation training. This helps connect awareness activities with measurable improvements rather than relying on training completion alone.
Strengthening the Human Firewall with Structured Phishing Simulation
Building a human firewall requires more than theoretical knowledge. Employees need opportunities to encounter realistic attack scenarios in a controlled environment so they can practise identifying suspicious messages and responding appropriately.
PhishCare, a phishing simulation and security awareness tool developed by CyberSapiens, supports this approach through simulated phishing campaigns designed to reflect common attack techniques. Scenarios can include impersonation attempts, urgent payment requests, and internal-style communications that resemble everyday business workflows.
Turn Simulated Threats Into Practical Learning
Structured phishing simulations help organisations observe employee responses, reinforce secure behaviour, and identify areas where additional awareness support may be beneficial.
Realistic Scenarios
Expose employees to controlled examples of suspicious emails and common social engineering tactics.
Timely Awareness Feedback
Provide learning feedback when employees interact with simulated phishing messages incorrectly, reinforcing recognition and safer decision-making.
Behavioural Insights
Review campaign results to identify recurring patterns, monitor changes, and determine where further training may help.
Repeating simulations throughout the year helps organisations reinforce learning rather than relying on a single awareness session. Reviewing results over time also gives security teams a clearer picture of employee responses and opportunities to improve the programme.
By combining realistic simulations with behavioural insights and ongoing education, organisations can make security awareness more practical and measurable. Phishing simulation reports can also provide supporting documentation for organisations working towards security and compliance objectives, alongside their broader controls and assessment processes.
Explore PhishCare for Your Organisation
Learn how phishing simulations can support employee awareness initiatives and help security teams understand behavioural trends across their organisation.
Measuring the Strength of Your Human Firewall
A human firewall should be assessed regularly to understand whether employees are becoming more confident at recognising and responding to cyber threats. Tracking behavioural indicators helps organisations evaluate awareness initiatives, identify weaknesses, and determine where additional support may be needed.
Phishing Simulation Failure Rates
Monitor how employees interact with simulated phishing messages over time. Changes in click rates can help identify progress and areas where further training may be beneficial.
Suspicious Email Reporting Rates
Measure how frequently employees report simulated or suspected phishing attempts through approved channels. Increasing reporting activity can indicate stronger employee engagement with security procedures.
Time to Report Suspicious Activity
Evaluate how quickly employees report potential threats after identifying them. Timely reporting gives security teams an opportunity to investigate and respond sooner.
Verification Behaviour
Assess whether employees verify unexpected requests, confirm sender identities, and follow established procedures before sharing sensitive information or approving transactions.
Turn Behavioural Data Into Better Decisions
Individual metrics provide useful signals, but they should be interpreted together. For example, a lower simulation click rate is more meaningful when employees also report suspicious messages promptly and follow verification procedures consistently.
Review results across campaigns and departments to identify recurring patterns, refine training activities, and communicate progress to relevant stakeholders. For organisations evaluating programme effectiveness, calculating the ROI of phishing simulation training can help connect programme costs with measurable outcomes and informed security investment decisions.
Behavioural measurement is an ongoing process, not a one-time assessment. By monitoring indicators consistently and using the findings to improve awareness initiatives, organisations can strengthen their human firewall and adapt to evolving threats.
The Human Firewall as a Strategic Advantage
Cyber threats will continue to evolve, and technology alone cannot eliminate every risk, particularly when attackers deliberately target human behaviour. Organisations that build a strong human firewall create a proactive layer of defence that complements technical security controls. Employees become active participants in protecting business systems, sensitive information, and organisational reputation.
A human firewall is not built overnight. It develops through consistent education, realistic practice, supportive leadership, and measurable improvement. When employees understand how to recognise suspicious activity, verify unusual requests, and report potential threats, security becomes a shared responsibility across the organisation.
From Security Awareness to Everyday Action
A stronger human firewall emerges when employees consistently apply what they learn. Organisations can reinforce this behaviour by focusing on three connected priorities.
Recognise
Identify suspicious messages, impersonation attempts, and unusual requests before taking action.
Verify
Confirm identities and validate unexpected requests through trusted communication channels.
Report
Report potential threats promptly so security teams can investigate and respond appropriately.
Ultimately, a human firewall is most effective when people and technology work together. By embedding security awareness into daily operations and continuously improving employee behaviour, organisations can build a more resilient defence against evolving cyber threats.
Frequently Asked Questions
1. What does the term human firewall mean?
A human firewall refers to employees who are trained to identify and respond appropriately to cyber threats such as phishing and social engineering attacks. It makes employees an active layer of organisational defence.
2. Why is a human firewall important?
Many cyberattacks exploit employee behaviour rather than technical vulnerabilities alone. A trained workforce can help recognise suspicious messages, verify unusual requests, and report potential threats before they cause further harm.
3. How do you measure the effectiveness of a human firewall?
Organisations can assess effectiveness through phishing simulation results, suspicious email reporting rates, time to report potential threats, and changes in employee verification behaviour. Reviewing these indicators together provides a more complete picture of progress.
4. Can a human firewall replace technical security tools?
No. A human firewall complements technical security controls such as firewalls, endpoint protection, encryption, and multi-factor authentication. Combining people, processes, and technology provides a more comprehensive approach to cybersecurity.
5. How often should organisations reinforce human firewall training?
Awareness should be reinforced continuously through periodic training, realistic phishing simulations, and ongoing behavioural measurement. The frequency and content should reflect the organisation’s risk profile, employee needs, and evolving threats.
Content Reviewed By
Mohammed Nawaz Sajjad
Sr. Security Analyst at CyberSapiens | Phishing Simulation | Ethical Hacker | Bug Hunter | Red Team
Nawaz specialises in phishing simulation campaigns, employee awareness assessments, red team exercises, and ethical hacking. He leads phishing simulation deployments at PhishCare, a product developed by CyberSapiens, supporting organisations in evaluating employee awareness and improving their response to phishing threats.
View LinkedIn ProfileStrengthen Your Human Firewall
Turn Employee Awareness Into Stronger Cybersecurity
Help employees recognise phishing attempts, practise safer decisions, and report suspicious activity with structured phishing simulations and security awareness initiatives from PhishCare.