Organisations increasingly invest in phishing simulation training to strengthen employee awareness and reduce cyber risk. However, security leaders often face an important challenge when presenting these initiatives to executives: demonstrating measurable return on investment (ROI). Unlike traditional technology purchases, the value of security awareness programmes is not always immediately visible in financial terms.
Phishing remains a significant cybersecurity threat, often serving as an entry point for credential theft, ransomware, financial fraud, and data breaches. The financial impact of a successful attack can extend beyond the initial loss to include incident response, operational disruption, legal expenses, and reputational damage.
Because phishing attacks frequently exploit human behaviour, employee awareness plays an important role in prevention. Phishing simulation training exposes employees to realistic attack scenarios in a controlled environment, measures their responses, and reinforces safer decision-making.
Calculating the ROI of phishing simulation training involves comparing programme costs with the estimated financial value of reduced risk. By analysing behavioural metrics, incident trends, and risk exposure, organisations can build a clearer picture of how awareness initiatives contribute to business resilience.
Key Insight
Turn Security Awareness Into Measurable Business Value
Effective ROI measurement combines programme costs, employee behaviour, and estimated changes in cyber risk. Tracking these indicators over time helps security teams explain the value of training while recognising that improved simulation results do not automatically guarantee fewer real-world incidents.
Understanding the Cost of Phishing Attacks
To calculate the ROI of phishing simulation training, organisations must first understand the potential financial impact of phishing incidents. These costs extend beyond direct financial losses and can affect business operations, customer relationships, and regulatory obligations.
A successful phishing attack may expose employee credentials, trigger fraudulent transactions, or introduce malware into business systems. Investigating and containing these incidents requires time and resources from security teams, IT personnel, and other stakeholders. Depending on the severity of the attack, organisations may also face customer notification expenses, legal consultation, regulatory consequences, and reputational damage.
Direct Financial Loss
Fraudulent payments, stolen funds, and compromised financial accounts can create immediate monetary losses for an organisation.
Incident Response
Investigations, credential resets, forensic analysis, system recovery, and external cybersecurity support can increase response costs.
Business Disruption
Downtime, delayed projects, interrupted services, and reduced productivity can create additional indirect costs.
Compliance and Reputation
Data exposure may lead to notification obligations, legal expenses, regulatory scrutiny, and reduced customer confidence.
Phishing threats can also take different forms depending on the organisation and its workforce. For example, employees should understand how targeted scams imitate official communications, including the techniques described in this guide to social security phishing scams.
Establish a Baseline Before Calculating ROI
Identify the relevant direct and indirect costs of phishing incidents, document available incident data, and estimate potential losses using realistic assumptions. A clear baseline makes it easier to evaluate whether an awareness programme is delivering measurable value.
Identifying the Key Metrics for ROI Calculation
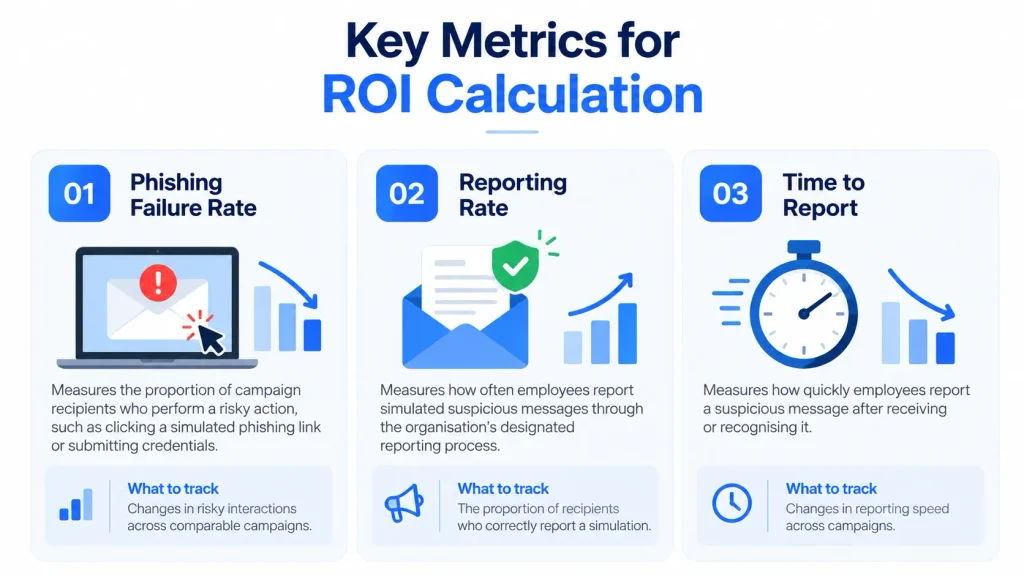
Calculating the ROI of phishing simulation training requires measurable indicators that show how employee behaviour changes over time. Tracking these metrics across multiple campaigns helps organisations evaluate programme effectiveness, identify recurring weaknesses, and make informed decisions about future training.
Rather than relying on a single result, security teams should evaluate several indicators together. Simulation interactions reveal how employees respond to controlled phishing scenarios, while reporting behaviour and response times provide additional insight into the organisation’s ability to recognise and escalate potential threats.
Phishing Failure Rate
Measures the proportion of campaign recipients who perform a defined risky action, such as clicking a simulated phishing link or submitting credentials.
What to track
Changes in risky interactions across comparable campaigns.
Reporting Rate
Measures how often employees report simulated suspicious messages through the organisation’s designated reporting process.
What to track
The proportion of recipients who correctly report a simulation.
Time to Report
Measures how quickly employees report a suspicious message after receiving or recognising it.
What to track
Changes in reporting speed across campaigns.
For meaningful comparisons, organisations should use consistent metric definitions, comparable campaign conditions, and a clear baseline. For example, a reduction in the phishing failure rate is more informative when campaign difficulty and employee participation are considered alongside the result.
Measure Behaviour, Not Just Clicks
A lower failure rate is only one indicator of progress. Combine simulation interactions with reporting behaviour, response speed, and real incident trends to build a more complete picture of awareness programme performance. These metrics support ROI estimates, but they do not independently prove that real-world attack risk has fallen by the same percentage.
Estimating Risk Reduction
After establishing baseline metrics, organisations can estimate how improved employee awareness may reduce the likelihood of a successful phishing attack. Simulation results provide useful behavioural indicators, but they should be considered alongside incident history, existing security controls, and the organisation’s threat exposure.
For example, if a phishing simulation failure rate decreases from 20% to 5%, the organisation has recorded a 15-percentage-point improvement. This represents a 75% relative reduction in the measured failure rate. However, it does not automatically mean that the probability of a real-world breach has fallen by 75%.
Example: Simulation Performance
Initial failure rate
20%
Later failure rate
5%
Relative reduction
75%
Illustrative example only. The figures describe simulated behaviour, not a verified reduction in real-world breach probability.
Translate Improved Performance Into Financial Risk Estimates
01. Estimate Baseline Risk
Use historical incidents, threat intelligence, business exposure, and existing controls to estimate the likelihood and potential cost of a phishing-related incident.
02. Assess Changes
Compare simulation outcomes over time and assess whether improved employee behaviour is supported by changes in actual incident data.
03. Calculate Expected Loss
Compare estimated losses before and after the programme, accounting for uncertainty and avoiding assumptions that simulation improvements directly equal breach-risk reductions.
Use Conservative, Evidence-Based Assumptions
Risk reduction estimates are more credible when they clearly state their assumptions, use realistic incident-cost estimates, and distinguish measured behavioural improvements from modelled financial benefits. This makes the resulting ROI calculation more useful for business leaders.
Calculating the Return on Investment
Once programme costs and estimated risk reduction have been assessed, organisations can calculate the potential ROI of phishing simulation training. The calculation compares the estimated financial benefit of avoided incidents with the total cost of running the programme.
Programme costs may include simulation software, employee training time, campaign administration, reporting, and follow-up learning activities. Financial benefits should be based on defensible estimates of reduced expected losses rather than assuming every improvement in simulation results translates directly into prevented incidents.
ROI Formula
ROI (%) = ((Estimated Benefits − Programme Costs) ÷ Programme Costs) × 100
For phishing simulation training, estimated benefits can be modelled as the reduction in expected phishing-related losses over a defined period. Avoid counting the same benefit more than once.
Example: Estimating Annual Programme ROI
Suppose an organisation spends $20,000 annually on phishing simulation training. Based on its risk assessment, it estimates that the programme reduces expected phishing-related losses by $50,000 per year. The figures below illustrate how that estimate would translate into ROI.
Calculation: (($50,000 − $20,000) ÷ $20,000) × 100 = 150%. This result depends on the estimated $50,000 benefit being reasonable, attributable to the programme, and measured over the same period as the costs.
Make Your ROI Case Credible
Use documented programme costs, transparent assumptions, and realistic estimates of avoided losses. Where the financial benefit is uncertain, present conservative, expected, and higher-risk scenarios rather than reporting a single projected saving as a guaranteed outcome.
Measuring Long-Term Value
Phishing simulation training can deliver benefits that extend beyond immediate risk reduction. When employees regularly practise identifying suspicious messages, they can become more familiar with common attack techniques and develop safer decision-making habits. Over time, these behaviours can contribute to a stronger security culture across the organisation.
Measuring long-term value requires organisations to look beyond individual campaign results. Reviewing behavioural trends, reporting patterns, and incident data over several months helps security teams assess whether awareness initiatives are producing sustained improvements.
Sustained Behavioural Improvement
Track whether risky interactions decline and employees consistently recognise suspicious messages across multiple simulation campaigns.
Stronger Threat Reporting
Assess whether employees report suspicious emails more frequently and promptly, helping security teams investigate potential threats earlier.
Better Resource Allocation
Use campaign results to identify recurring weaknesses, prioritise targeted training, and direct security resources towards areas of greater risk.
Long-term measurement also helps organisations evaluate whether their programmes remain relevant as phishing techniques change. Reviewing campaign outcomes, updating scenarios, and providing additional training where needed can help maintain employee awareness over time.
Evaluate Progress Beyond a Single Campaign
Compare results over time, account for changes in campaign difficulty and employee participation, and review actual security incidents alongside simulation data. These measures help organisations build a more reliable picture of programme effectiveness and its potential business value.
Supporting ROI Measurement With PhishCare
Accurate ROI measurement depends on reliable behavioural data and consistent programme reporting. Phishing simulation platforms help organisations evaluate how employees respond to controlled phishing scenarios, identify recurring weaknesses, and assess changes in awareness over time. PhishCare supports this process through phishing simulation campaigns and reporting insights that help security teams understand employee interactions.
By reviewing campaign outcomes across departments and reporting periods, organisations can identify where employees may need additional guidance. These insights can support decisions about training priorities, campaign frequency, and the allocation of security awareness resources.
Behavioural Reporting
Review available campaign metrics, including simulated link interactions and reporting behaviour, to understand how employees respond to phishing scenarios.
Targeted Learning
Use observed weaknesses to guide follow-up training and reinforce recognition of suspicious links, deceptive messages, and credential requests.
Progress Tracking
Compare campaign results over time to assess behavioural trends and support evidence-based decisions about the awareness programme.
Apply Simulation Insights to Different Business Environments
The way organisations design and evaluate phishing simulations can vary according to their workforce, regulatory environment, and operational risks. Businesses assessing regional practices can explore the phishing simulation market in the Philippines for additional context on the growing adoption of employee testing and awareness initiatives.
Organisations operating in Germany can also review phishing simulation considerations under GDPR and NIS2 when aligning awareness activities with broader compliance and risk management objectives.
For businesses in Saudi Arabia, the guidance on phishing simulation, regulatory context, and best practices offers another regional perspective on structuring employee awareness initiatives.
From Data to Decisions
Make Security Awareness Measurable
Use simulation reports to track employee behaviour, identify knowledge gaps, and evaluate progress over time. Combine these findings with programme expenses and realistic risk estimates to develop a more defensible ROI assessment.
Turning Awareness Into Measurable Business Value
Cybersecurity awareness programmes are often viewed as compliance requirements rather than strategic investments. However, when organisations measure employee behaviour, programme costs, and estimated changes in risk exposure, phishing simulation training can become a more measurable part of their cybersecurity strategy.
Calculating ROI helps security leaders explain the potential business value of awareness initiatives and make better-informed decisions about continued investment. It also encourages teams to review programme performance regularly instead of relying on isolated campaign results or participation figures alone.
Track Meaningful Metrics
Monitor simulation failure rates, employee reporting behaviour, time to report, programme costs, and relevant incident trends.
Estimate Financial Benefits
Use documented assumptions and realistic loss estimates to assess potential reductions in expected phishing-related costs.
Improve Continuously
Review results over time, adapt simulation scenarios, and provide targeted learning where recurring weaknesses are identified.
The strongest ROI assessments combine measurable behavioural improvements with realistic financial modelling. Although phishing simulations cannot eliminate cyber risk or guarantee a specific financial return, they can provide valuable evidence to guide awareness programmes and support broader risk management decisions.
Final Takeaway
Measure the Impact. Strengthen the Human Layer of Security.
By tracking employee behaviour, evaluating programme expenses, and using evidence-based risk estimates, organisations can make a stronger business case for phishing simulation training and build a more resilient security culture.
FAQs About Phishing Simulation ROI
Learn how to measure the effectiveness, financial value, and long-term benefits of phishing simulation training.
1. What is the ROI of phishing simulation training?
ROI measures the estimated financial benefits of phishing simulation training relative to its costs. Organisations can assess it by comparing programme expenses with the estimated reduction in phishing-related losses, using documented assumptions and realistic risk estimates.
2. How can organisations measure the effectiveness of phishing training?
Organisations can track simulation failure rates, suspicious email reporting rates, time to report, repeat mistakes, and relevant incident trends. Comparing these indicators across campaigns helps identify behavioural improvements and areas requiring further training.
3. Why is ROI important for security awareness programmes?
ROI helps security leaders explain programme costs, evaluate potential financial benefits, and justify continued investment in employee awareness. It also supports more informed decisions about training priorities and security resources.
4. Can phishing simulation completely eliminate phishing risk?
No. Phishing simulations can improve employee awareness and help identify risky behaviours, but they cannot eliminate phishing threats. Organisations should combine training with email security, multi-factor authentication, access controls, and incident response procedures.
5. How often should organisations run phishing simulation campaigns?
Organisations should conduct simulations regularly throughout the year, with frequency based on their risk exposure, workforce needs, and programme objectives. Repeated campaigns help teams track behavioural trends and reinforce learning over time.
About the Author
Mohammed Nawaz Sajjad
Mohammed Nawaz Sajjad writes about cybersecurity, phishing simulation, employee awareness, and practical approaches to managing organisational cyber risk.
Connect on LinkedIn →Make Phishing Simulation ROI Measurable
Strengthen employee awareness, measure behavioural outcomes, and use meaningful security metrics to support better cyber risk management decisions.
Talk to Our Team Explore Plans