Cyber security awareness programs are common across organisations, yet employees do not always report suspicious emails. Without timely reporting, security teams lose valuable visibility and time when responding to potential threats.
A reporting-first security culture moves beyond recognising phishing attacks to encouraging employees to take action. When suspicious messages are reported quickly, security teams can investigate potential threats and respond before they affect more people.
Phishing attacks continue to exploit urgency, authority and routine business processes. Even with email filtering in place, some malicious messages may reach employee inboxes. Employee reporting therefore plays an important role in strengthening organisational cyber security.
Key Takeaway
Awareness matters. Reporting turns it into action.
A strong reporting culture makes it easier for employees to escalate suspicious activity, helping security teams investigate sooner and improve threat visibility.
Why Reporting Is Critical for Cyber Security
Early detection helps organisations limit the potential impact of cyber attacks. When an employee reports a suspicious email quickly, security teams can investigate it, identify similar messages and take steps to prevent other employees from interacting with the same threat.
Faster Threat Detection
Prompt reporting helps security teams investigate suspicious messages before more employees interact with them.
Improved Threat Intelligence
Employee reports reveal emerging phishing techniques and help security teams refine detection rules and awareness training.
Reduced Potential Impact
Early escalation can help prevent credential theft, fraudulent payment approvals and malicious downloads from causing further damage.
As attackers increasingly use AI to create convincing messages, employees need to stay alert and report suspicious communications. Explore how generative AI is changing phishing attacks in 2026 to understand how these threats continue to evolve.
Reporting creates visibility
Without employee reports, suspicious messages may go unnoticed until an incident occurs. A reporting-first approach gives security teams an earlier opportunity to investigate, respond and strengthen organisational defences.
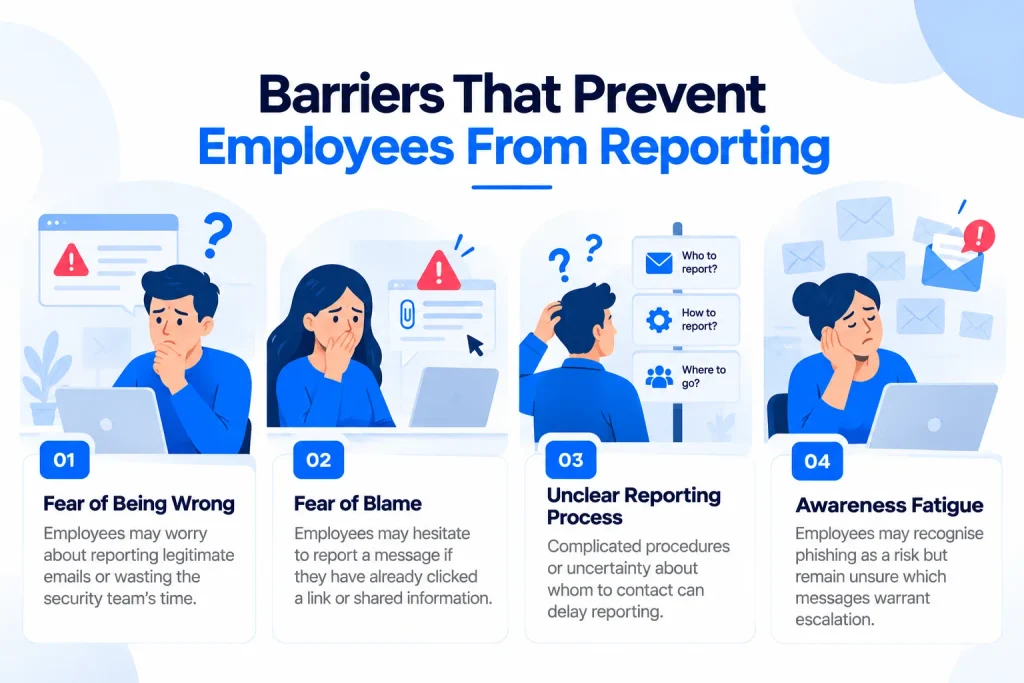
Barriers That Prevent Employees From Reporting
Even when employees understand phishing risks, uncertainty and workplace habits can prevent them from reporting suspicious messages. Identifying these barriers is an important step towards building a stronger reporting culture.
Barrier 01
Fear of Being Wrong
Employees may worry about reporting legitimate emails or wasting the security team’s time.
Barrier 02
Fear of Blame
Employees may hesitate to report a message if they have already clicked a link or shared information.
Barrier 03
Unclear Reporting Process
Complicated procedures or uncertainty about whom to contact can delay reporting.
Barrier 04
Awareness Fatigue
Employees may recognise phishing as a risk but remain unsure which messages warrant escalation.
Make reporting safe and straightforward
Organisations can address these barriers by simplifying reporting procedures, encouraging employees to speak up without fear of blame, and reinforcing that suspicious messages are worth reporting even when the threat is uncertain.
The Principles of a Reporting-First Security Culture
Building a reporting-first culture requires clear processes, positive reinforcement and leadership support. Employees should know how to report suspicious activity and feel confident that their efforts are valued.
Principle 01
Make Reporting Simple
Provide a clear, accessible process so employees can report suspicious emails without navigating complicated procedures.
Principle 02
Encourage, Don’t Criticise
Recognise employees who report suspicious messages, even when an investigation confirms that the message is harmless.
Principle 03
Lead by Example
When leaders emphasise verification and reporting, they reinforce the importance of secure behaviour across the organisation.
Principle 04
Focus Training on Action
Teach employees not only how to recognise phishing indicators, but also what steps to take when they encounter a suspicious message.
Leadership sets the tone
A reporting-first culture works best when employees see reporting as a valued security practice. Leadership support and clear accountability help turn this expectation into an everyday habit.
Learn how board members evaluate cyber awareness programsReinforcing Reporting Through Practical Experience
Practical experience helps employees become familiar with phishing techniques and understand how to respond. Simulated phishing campaigns provide a controlled way to practise recognising suspicious messages and reporting them.
Step 01
Practise Recognition
Employees encounter simulated messages that reflect common phishing techniques and business communication patterns.
Step 02
Reinforce Reporting
Employees practise escalating suspicious messages, helping make reporting a familiar part of their routine.
Step 03
Build Confidence
Feedback helps employees understand missed warning signs and improve their responses to future suspicious messages.
Turn practice into a reporting habit
Consistent simulations and constructive feedback help reinforce the expectation that suspicious messages should be reported promptly. Over time, reporting can become a routine part of everyday security behaviour.
The Role of Measurement in Reporting Culture
Measuring employee reporting behaviour helps organisations understand whether security awareness programs are leading to meaningful action. Tracking reporting trends over time can reveal improvements, highlight gaps and guide future training.
Metric 01
Reporting Rate
Track the proportion of employees who report simulated phishing emails to assess whether they are taking action.
Metric 02
Time to Report
Measure how quickly employees escalate suspicious messages. Faster reporting can help security teams investigate potential threats sooner.
Metric 03
Correct Escalation Rate
Review how often employees correctly identify and report simulated phishing messages rather than overlooking or interacting with them.
These metrics become more useful when reviewed across repeated campaigns. Organisations can compare results over time, identify teams that need additional support and assess whether training is improving reporting behaviour.
Reporting metrics should also be considered in the context of how employees work. Organisations with distributed teams can explore phishing threats in remote work environments to understand why consistent employee vigilance matters across different working arrangements.
Connect reporting metrics to business value
Consistent reporting data helps organisations evaluate progress and make informed decisions about awareness initiatives. To understand the financial perspective, explore this comparison of cybersecurity training versus data breach costs.
Reporting metrics should be interpreted alongside other security indicators. Improvements in simulated campaigns provide evidence of behavioural progress, but they do not guarantee that every real phishing attack will be detected.
Strengthening Reporting Behaviour With PhishCare
Building a reporting-first security culture requires continuous reinforcement and practical exposure to phishing scenarios. PhishCare, a phishing simulation and awareness platform developed by CyberSapiens, helps organisations reinforce employee awareness through simulated phishing campaigns.
From Awareness to Action
Practise. Learn. Improve.
Realistic simulations give employees opportunities to recognise suspicious messages, practise reporting and learn from their responses in a controlled environment.
Capability 01
Realistic Phishing Simulations
Simulated impersonation attempts, urgent payment requests and routine-looking business messages help employees practise recognising potential threats.
Capability 02
Immediate Learning Feedback
When employees interact incorrectly with a simulated phishing email, feedback can help explain missed warning signs and reinforce safer behaviour.
Capability 03
Behavioural Reporting Insights
Reporting insights help security teams review employee responses across departments and identify where additional awareness support may be beneficial.
By combining practical simulations, learning feedback and behavioural insights, organisations can evaluate how their awareness initiatives support reporting habits and identify opportunities for improvement.
Make employee reporting part of everyday security
Consistent reinforcement helps employees understand that reporting suspicious messages is a valuable contribution to organisational security. PhishCare can support this process through structured phishing simulation and awareness activities.
Talk to the PhishCare TeamTurning Awareness Into Action
Cyber security awareness programs are most effective when they lead to measurable action. Teaching employees to recognise phishing attacks is important, but encouraging them to report suspicious activity helps security teams identify and investigate potential threats sooner.
Encourage Prompt Reporting
Make reporting simple, accessible and supported so employees feel confident escalating suspicious messages.
Reinforce Secure Behaviour
Use practical simulations and constructive feedback to help employees practise recognising and reporting phishing attempts.
Measure Progress
Monitor reporting rates, time to report and correct escalation to identify improvements and areas requiring further support.
The Key Takeaway
A stronger security culture starts with employees who take action.
When employees understand that reporting is expected, valued and supported, they become active participants in organisational defence. Combining awareness, practical experience and measurement helps turn reporting into a routine security behaviour.
Frequently Asked Questions
1. What is a reporting-first security culture?
A reporting-first security culture is an organisational environment where employees are encouraged to report suspicious emails and potential cyber threats promptly.
2. Why is employee reporting important in cyber security?
Employee reporting helps security teams identify suspicious messages earlier, investigate potential phishing attacks and take steps to limit their impact.
3. How can organisations encourage employees to report phishing emails?
Organisations can simplify reporting procedures, provide practical awareness training, recognise employee vigilance and create a supportive environment where employees can report mistakes without fear of blame.
4. Should employees report emails even if they are unsure?
Yes. Employees should report messages that appear suspicious, even when they are uncertain. Security teams can assess the message and determine whether further action is necessary.
5. How can organisations measure improvements in reporting culture?
Organisations can monitor reporting rates, time to report suspicious emails and the proportion of simulated phishing messages correctly identified and escalated.
Content Reviewed By
Mohammed Nawaz Sajjad
Sr. Security Analyst at CyberSapiens | Phishing Simulation | Ethical Hacker | Bug Hunter | Red Team
Nawaz specialises in phishing simulation campaigns, employee awareness assessments, red team exercises and ethical hacking. His work focuses on evaluating employee responses to phishing threats and supporting practical security awareness initiatives.
View LinkedIn ProfileStrengthen Your Security Culture
Turn Employee Awareness Into Action With PhishCare
Encourage employees to recognise and report suspicious messages through practical phishing simulations and awareness activities. Strengthen reporting habits with a consistent, measurable approach to employee security.